Rabu, 21 Oktober 2026

Local AI Weekly #6: If You Can Reverse Engineer It, It's Open Source!

Reverse Engineering with AI

What I realized in the past week or so is that if you can reverse engineer it, any software is open source software.

Not in the license sense, of course. But AI agents are getting good at reading binaries, tracing what an app does and rebuilding it. Last issue, we had the Craft tools cloning Microsoft Office. This week, there are more office clones, a viral repo that reverse engineers "anything", and people taking back control of their smart TVs with the help of AI.

The source code is no longer the wall it used to be. Whether that's a good thing depends a lot on which side you are on.

🧪 On my desk

I have enjoyed using Myna for voice based input on Ubuntu 26.04 (yes, it can be installed on 26.04). The performance is surprising good. Next, I will be trying a few more such voice input tools, starting with SpeakoFlow.

🔍 Discover AI tools

REA (Reverse Engineer Anything) is the repo of the week. It's an MIT-licensed MCP server that lets AI agents inspect native binaries, Electron apps, Android APKs, firmware and more. Deep native analysis needs proper reverse engineering tools like Ghidra. Analysis runs locally, but your agent's model provider still sees what it finds. Also, fake REA repos are already serving malware, so install it only from the official repo or npm package.

Graphify is reverse engineering for your own code. It turns a codebase, docs and PDFs into a knowledge graph your coding agent can query. Code is parsed locally with tree-sitter, and GRAPHIFY_BACKEND=ollama keeps the rest local too.

It's a Plan is a self-hosted Linear/Jira alternative where AI agents get a role and pick up issues like any team member. External agents run on your machine and hand tasks to Claude Code, Codex or opencode. In early stages for now.

🏢 The office clone wars

Mandrake Linux creator Gaël Duval is behind ElixirOffice, a Microsoft Office look-alike built on Euro-Office components. The code was written by LLM agents, with tests and reviews on every change. It's AGPL-3.0 and in beta.

Then there is Ely Office, six offline desktop apps for documents, sheets, slides, PDF, Git and Markdown.

And BetterOffice, which we covered last week, now has its Apache-2.0 source under the openooxml org on GitHub.

Meanwhile, Perplexity added REA to its Computer agent as a /reverse-engineer command, free until 31 October. Its demo clones included Photopea, Audacity and... LibreOffice Calc. Yes, reverse engineering an app that is already open source (LOL).

📺 Your TV, your rules

My favorite story of the week. Android TV owners are using AI to debloat their smart TVs. The agent connects over ADB, lists installed packages and disables ads, telemetry and preinstalled junk. People report faster TVs. A related project does the same for Fire TV.

This is the "reverse engineering" idea at its most useful. You don't need to be an Android developer anymore to fix the device you paid for.

📡 Open Model News

Meta released Muse Spark Open, an 816B model with 42B active parameters and a 1M-token context. The headline says it "runs on Macs". But that actually means two Mac Studios with 512 GB each. Not the kind of hardware normies like me can afford.

Also note the licence. It's the "Muse Model License" with limited commercial terms. Open weights, yes. Open source, no.

👀 Big Tech Watch

NVIDIA RTX Spark laptops went on sale on 16 October, starting at $2,599, from ASUS, Dell, HP, Lenovo, Microsoft and MSI. The chip pairs a Blackwell GPU with a Grace Arm CPU and up to 128GB of unified memory, enough for bigger local models on a laptop. Two catches. The 128GB is only on the top configuration, and the lower tier tops out at 32GB. And these are Windows on Arm machines, with no word on native Linux support (yet).

Google Research open sourced Harness², a framework that improves the harness around a model (prompts, tools, memory, skills) without touching its weights. It's Apache-2.0 and uses OpenCode by default. Model runs are configured for Vertex AI, and I see no documented local model path yet.

Anthropic says Claude Code now gzips the conversation it sends on every turn, and cloud sessions start as soon as you begin typing. It reports up to 3x faster time to first token for local Claude Code sessions, compared with August. The billion-dollar AI speedup came from gzip, a free and open source software tool from 1992.

🗂 AI Jargon: Clean-room design

How do you copy software legally? Clean-room design.

One team studies the original app and writes down only what it does: the behavior, the file formats, the interfaces. A second team, which has never seen the original code, builds a new app from that description. That separation is what protects the clone from copyright claims. It's how the PC BIOS was cloned in the 1980s and that's how Compaq became a popular PC brand.

AI agents blur this neatly. The same agent that reads the binary often writes the new code. Whether that still counts as a clean room is a question lawyers will be busy with for a while.

😂 Meme
⚡ Quick Tip: Back up before an agent touches your TV

Before you get too excited and let an agent debloat your Android TV, save the package list first:

adb shell pm list packages > tv-packages.txt

Ask the agent to use pm disable-user instead of uninstalling. A disabled package comes back with adb shell pm enable <package-name>. And turn off USB or wireless debugging when you are done. An open ADB port on your home network is not something you want to leave lying around.

And if you must use cloud AI for something sensitive, Maple has a sensible guide to using AI privately. Maple sells a private AI service, so keep that in mind. The thing is that privacy settings alone don't stop a provider from reading your chats. Running models locally is still the only option that keeps your words off someone else's server.

Keep on exploring AI (locally).


from It's FOSS https://ift.tt/w1yihTD
via IFTTT

DankMaterialShell Becomes Dux Shell as Dank Linux Rebrands to Dux Labs

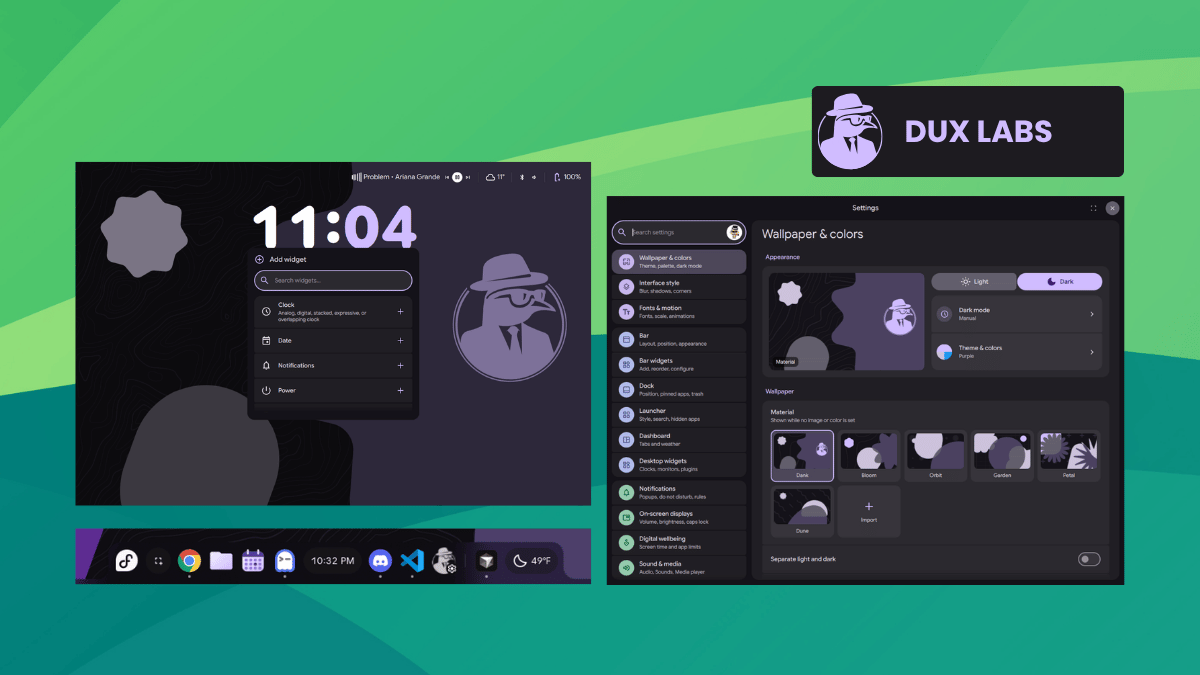
dms and dank linux rebrand banner

Dank Linux, the Wayland desktop suite built around DankMaterialShell (DMS), has put out its final post on X under that name, bidding farewell to its old identity. Accompanying it is DMS 2.0, codenamed "Heisenberg," which reached GitHub just a few hours ago.

If you didn't already know, the shell is a Quickshell and Go project that stands in for tools like waybar, swaylock, mako, and fuzzel. Around it sit a greeter, a calendar app, a system monitor, and a search service.

It began as a hobby project, with 1.0 shipping in December last year. Since then, newer releases have added niceties like desktop widgets, a new launcher, and spring-based motion.

With that many components in the suite, the project has now put all of them under a new name.

A surprise rebrand

The rebranding covers the whole suite. DMS is now Dux Shell, and the greeter, search tool, system monitor, and calendar are now Dux Greeter, Dux Search, Dux GOP, and Dux Calendar, respectively.

Dank Linux gets renamed Dux Labs, which also acts as the new name for the project as a whole and for every app in the suite.

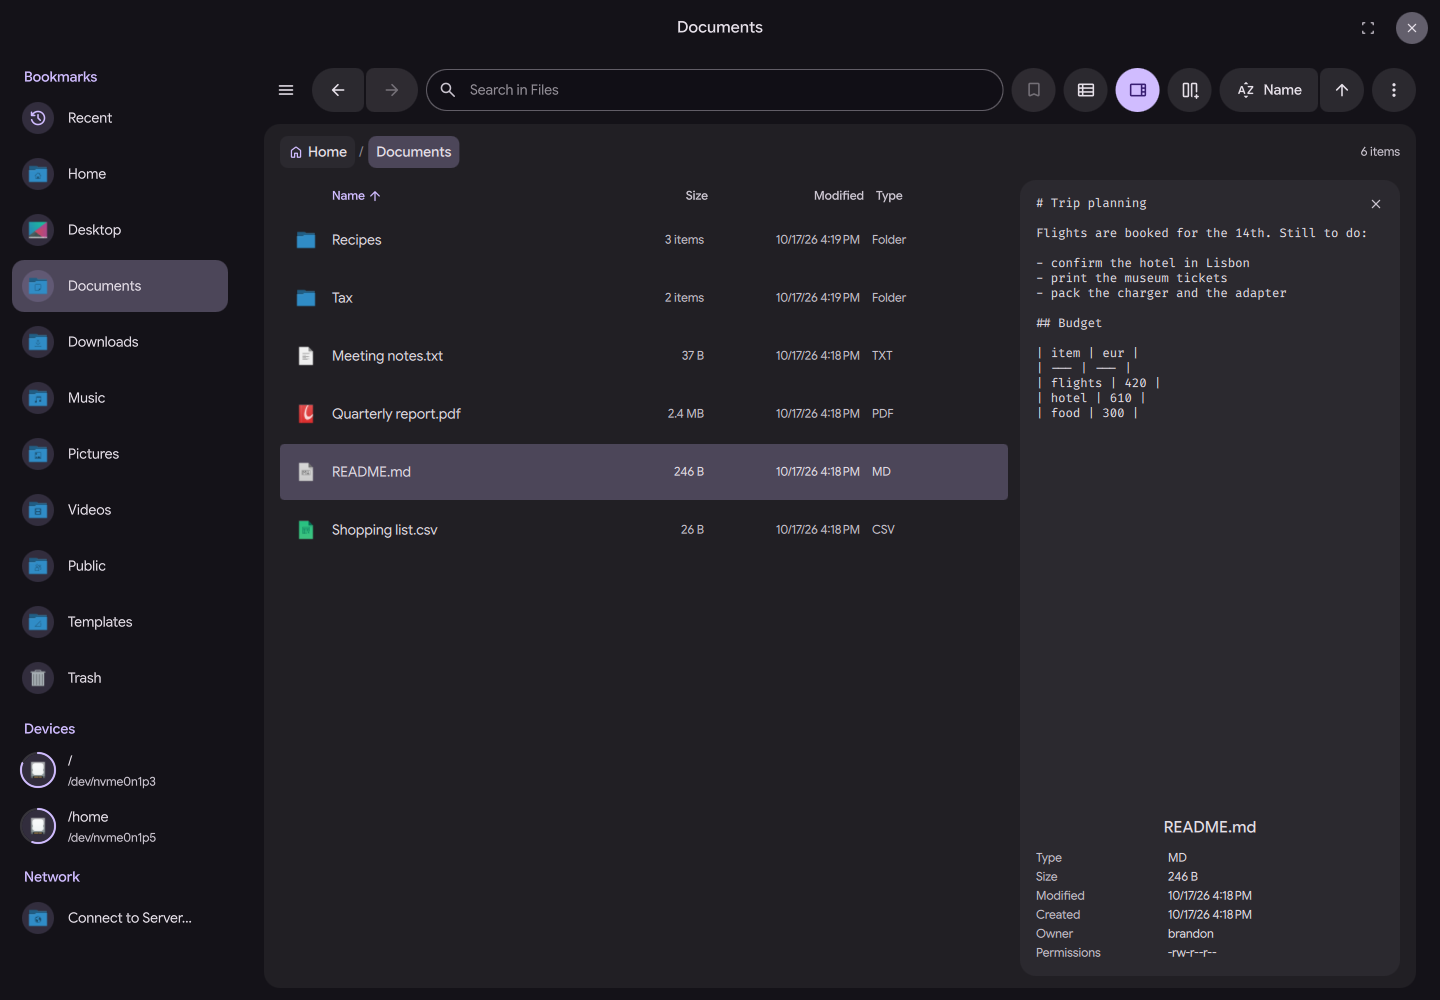
Dux Files is a standalone file manager that is the one piece that's new instead of being renamed. It offers features like tabs, split views, trash, and network shares. It picks up your DMS theme if the shell is running.

Dux is the suite's mascot, and the name echoes Linux's penguin mascot, Tux. Starting with a D also lets the dms, dcal, and dgop commands keep their names.

The project's reasoning to go through the rebrand is that a name built around one product no longer fits a suite with its separate collection of apps and a plugin community.

Another thing to note is that the earlier release, DMS 1.6, still carried the Dank name, and its roadmap listed a standalone file browser and phone integration, but a rename was never really mentioned.

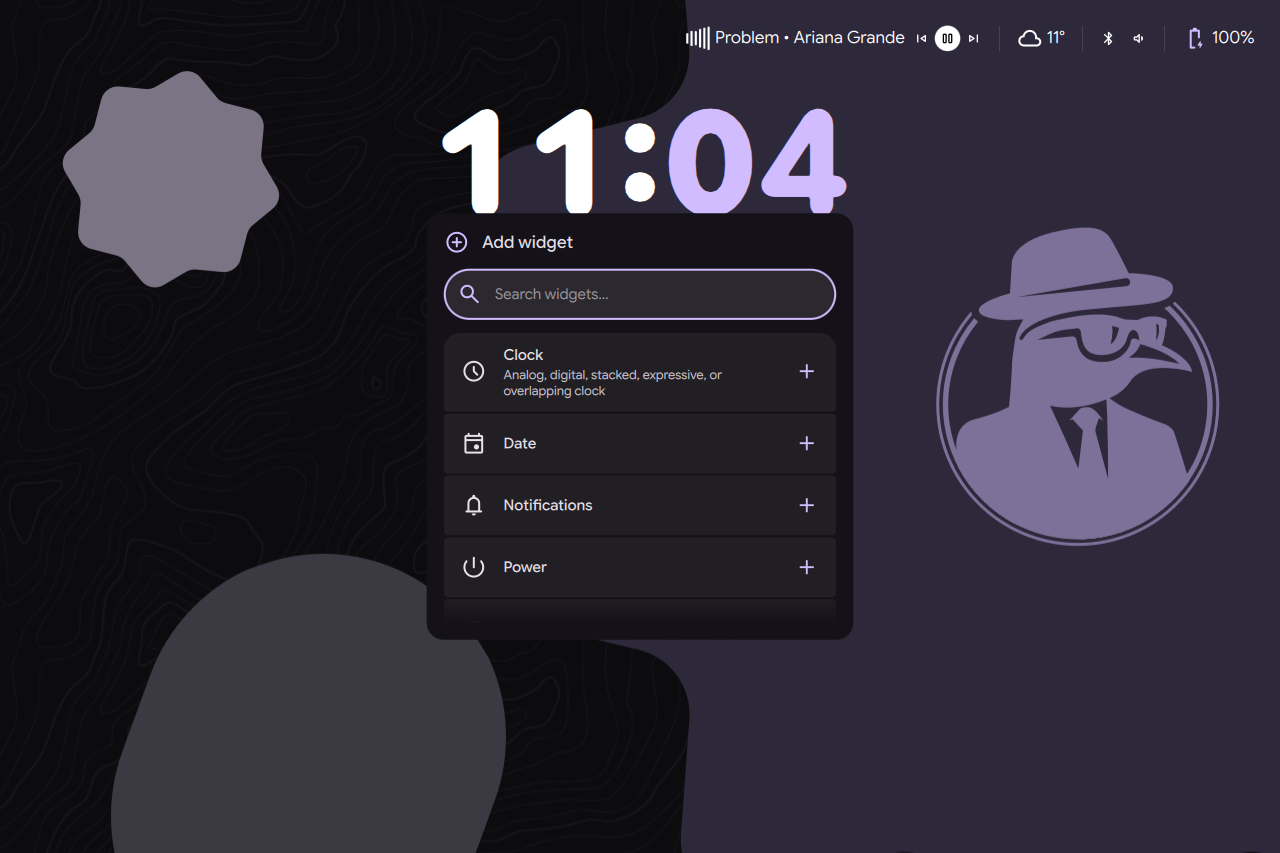
As for the DMS 2.0 release, it is a packed one that adds a Material 3 Expressive redesign, plugins for the dashboard and dock, and a lock screen with widgets you can arrange yourself.

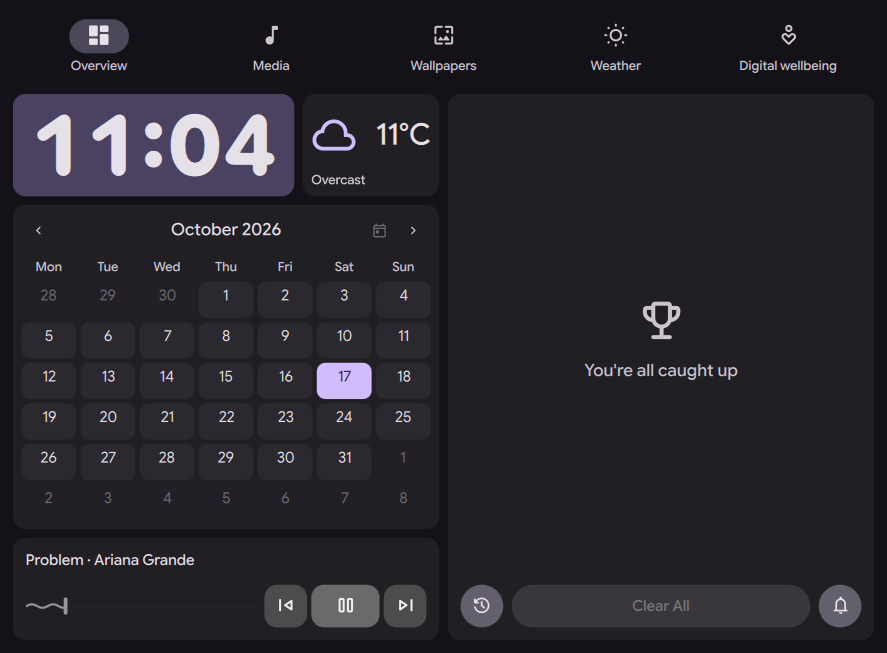
It also adds Dux Dot, a free-floating companion or replacement for the bar that can turn into notifications, weather, media, and wallpaper views, as well as the control center, dashboard, and launcher.

What now?

The project has already moved from the AvengeMedia umbrella to a new GitHub organization called Dux Labs.

You will find many repositories that used to be known by their Dank names, including dux-shell (previously DankMaterialShell), dux-gop (dgop), dux-search (danksearch), dux-calendar (dankcalendar), and dux-greeter (dank-greeter).

Personally, I preferred the Dank branding. But if the developers feel this is the best approach and the community accepts it, there's no point talking about what was.


Suggested Read 📖: CutefishOS is back with a vibe-coded desktop.


from It's FOSS https://ift.tt/LZHc9fy
via IFTTT
Save Upto 40% on Kubernetes Security Certifications From the Linux Foundation

If you have been planning to get a certification, this is the week to do it. The Linux Foundation is running its Cyber Security Month promo, and you can get up to 40% off on cyber security certifications, training courses and the THRIVE-ONE e-learning subscription.

Linux Foundation is the official organization behind Linux, Kubernetes, and many other industry-facing projects. Their certifications are well respected across countries and enterprises.

The offer ends on October 23, 2026 at 23:59 UTC. That gives you just a couple of days to make up your mind.

The good thing is that you have one full year to take the certification exam. So, you can purchase the cert exams today to save the money, prepare in a few weeks/couple of months and then attempt the exam.

There is also a 3 day money back guarantee with some conditions. Please read the policy here.

This article contains affiliate links. Please read our affiliate policy.

Your discount codes

Here are the codes. They are specific to It's FOSS readers, so use these and not the generic ones you see on the promo page.

Discount Applies to Code
40% off Cybersecurity certifications, bundles and courses (full list on the promo page) OCT26CYBERFOSS
35% off All other Instructor-led Training, Certifications and Courses by Technology OCT26NONCYBERFOSS
30% off THRIVE-ONE Annual (new subscriptions only) OCT26THRIVEFOSS

So if you are eyeing CKA, LFCS or any other Linux Foundation certification that is not in the cybersecurity list, you still get 35% off with the second code.

Even if the offer ends, you can always get 30% off with our special coupon code: ITSFOSS.

💡
Apply the code on the checkout page. The discount is for new, individual purchases only and cannot be combined with other offers.

Kubernetes Security Certifications

The biggest savings this time are on the Kubernetes security certifications. Here are the ones worth looking at.

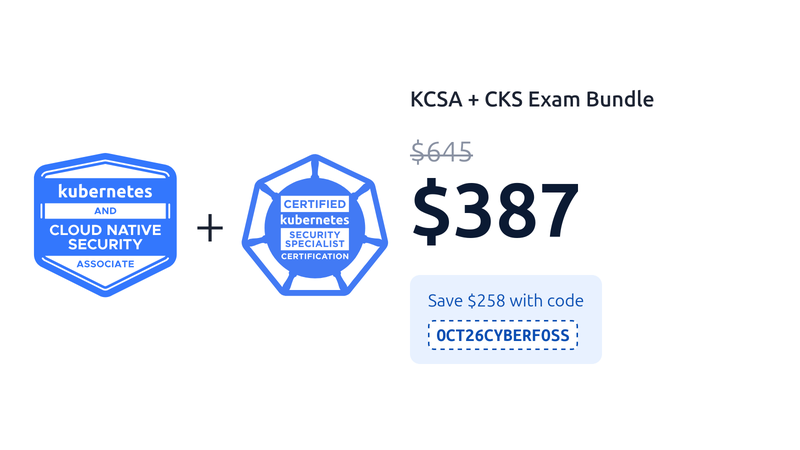
KCSA + CKS bundle: $645 $387

KCSA + CKS exam bundle page on the Linux Foundation

This bundle groups two certification exams together: Kubernetes and Cloud Native Security Associate (KCSA) and Certified Kubernetes Security Specialist (CKS). You save $258 over the regular bundle price.

KCSA is the entry-level, multiple choice exam. CKS is the hands-on, professional one. Taking them in this order makes sense, as KCSA builds the foundation that CKS expects from you.

Keep in mind that you must have passed the Certified Kubernetes Administrator (CKA) exam before you can take CKS. If you don't have CKA yet, you can grab it with the 35% code OCT26NONCYBERFOSS.

You can also choose to get either of the certification exams instead of the bundle. But if you are getting both, the bundle saves you additional money.

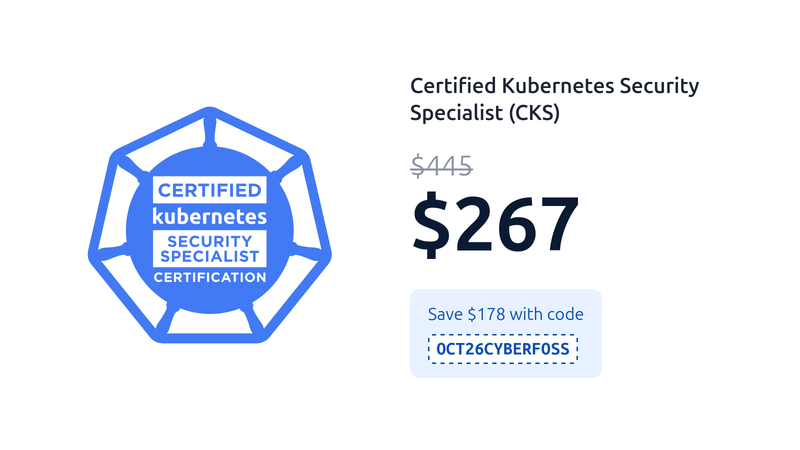
Certified Kubernetes Security Specialist (CKS): $445 $267

Certified Kubernetes Security Specialist (CKS) offer on the Linux Foundation

CKS is a 2-hour, performance-based exam. You solve real tasks on a live Kubernetes cluster from the command line, so there is no guessing your way through multiple choice options.

You also get two sessions on the Killer.sh exam simulator to practice in an environment similar to the real exam. The certification is valid for 2 years. As mentioned above, an active CKA is a prerequisite.

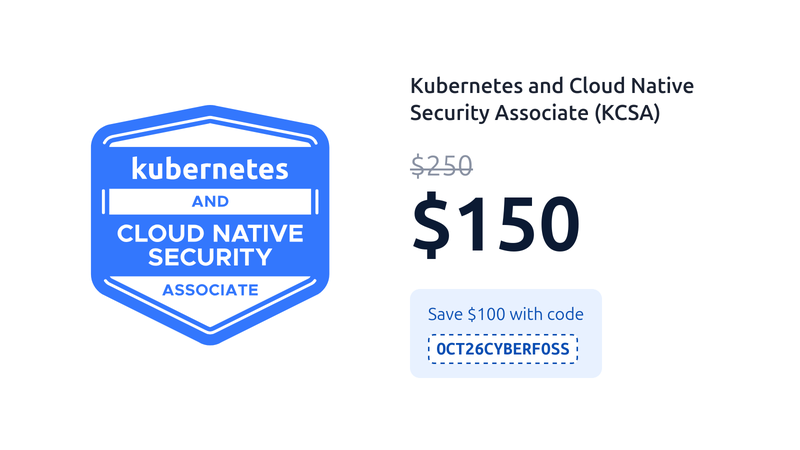
Kubernetes and Cloud Native Security Associate (KCSA): $250 $150

Kubernetes and Cloud Native Security Associate (KCSA) offer on the Linux Foundation

KCSA is a pre-professional certification for people starting out in cloud native security. It is a 90-minute, online proctored, multiple choice exam with no prerequisites.

At $150, this is the most affordable way to get a Linux Foundation security certification on your resume this month. You save $100.

THRIVE-ONE Annual (e-learning): $360 $252

THRIVE-ONE subscription plans on the Linux Foundation

THRIVE-ONE is the Linux Foundation's subscription. The annual plan gives you unlimited access to the entire e-learning catalog for a year, plus all SkillCred exams.

You also get a 40% coupon for any certification or course and 50% off guaranteed-to-run instructor-led courses. Note that certification exams themselves are not included in the subscription.

This works well if you want to learn several technologies over the year instead of focusing on one exam. The 30% discount applies to new subscriptions only.

Why get certified at all?

I get asked this a lot. Are Linux certifications worth it?

A certification is a way to prove to a recruiter that you have the skill. Anyone can list "Kubernetes" or "Linux administration" on a resume. A certification from an industry-recognized body like the Linux Foundation tells the hiring manager that someone has actually tested you on it.

This matters even more for performance-based exams like CKA, CKS and LFCS. You don't pick answers from a list. You fix real problems on a live system within a time limit, which is pretty much what the job looks like.

Certifications are even more helpful if you are a fresh graduate, or if you are switching to a new domain like cloud native or security.

And it is not just my opinion. In the Linux Foundation’s 2026 State of Tech Talent report, 76% of organizations said they value certifications when assessing candidates for a technical role. That is slightly ahead of college degrees at 74%, and this is the third year in a row that certifications have ranked above degrees.

You don't have to take the exam this week

This is the part a lot of people miss. You only need to buy the certification before October 23. You don't need to take the exam right away.

Linux Foundation certifications come with 12 months of exam eligibility. You can schedule and take the exam any time within a year of purchase. So you can lock in the discounted price now and prepare at your own pace.

Most certifications also include one free retake. If your first attempt does not go well, you get a second chance without paying again. That's a big relief, in my opinion.

Missed the deal? Use our evergreen code

If you are reading this after October 23, don't worry. It's FOSS readers have a code that works any time, even when no promo is running.

💡 Use the code ITSFOSS to get 30% off on Linux Foundation certifications, e-learning courses and bundles. Valid all year round.

Let me know in the comments if you encounter any inaccuracies or if you have questions.


from It's FOSS https://ift.tt/TxAi5jc
via IFTTT
Selasa, 20 Oktober 2026

Microsoft’s AI Coding Agent Testing Tool Has Been Open-Sourced

microsoft scope deployment banner

Coding agents now decide which SDK to use and which tools to call, though something that works smoothly for a human developer can still leave an agent stumbling.

Microsoft built Scope to find those failures. It runs the same task through different agents and scores what each one produces. The code for it is provided under the MIT license.

They are calling it the field Developer Agent Experience, or DevAx, though its 'scope' is to evaluate existing coding agents.

How does it work?

microsoft scope demo

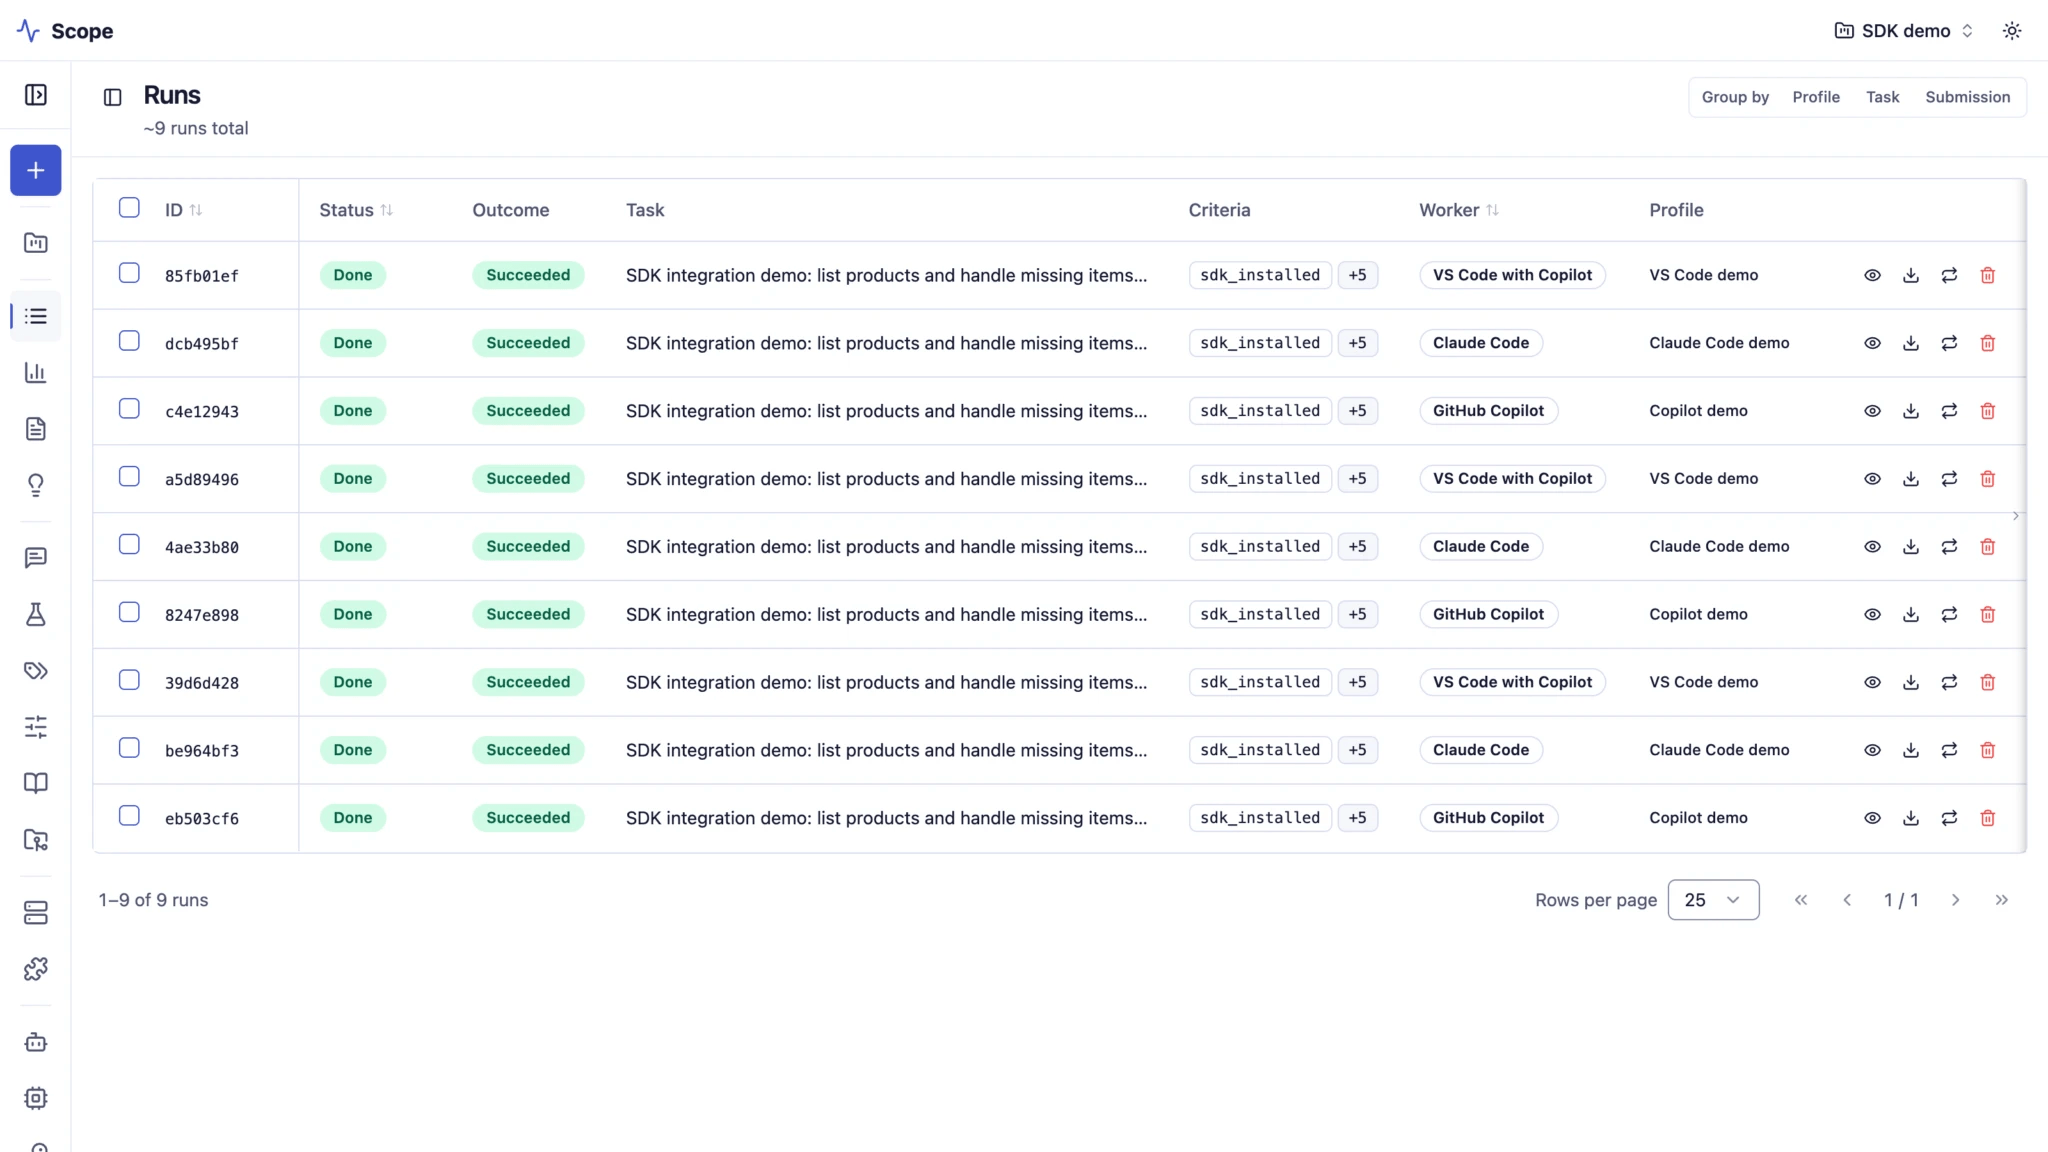
You give Scope a task, a starting codebase if needed, and an agent setup. It then drives existing agents such as GitHub Copilot and Claude Code through that task.

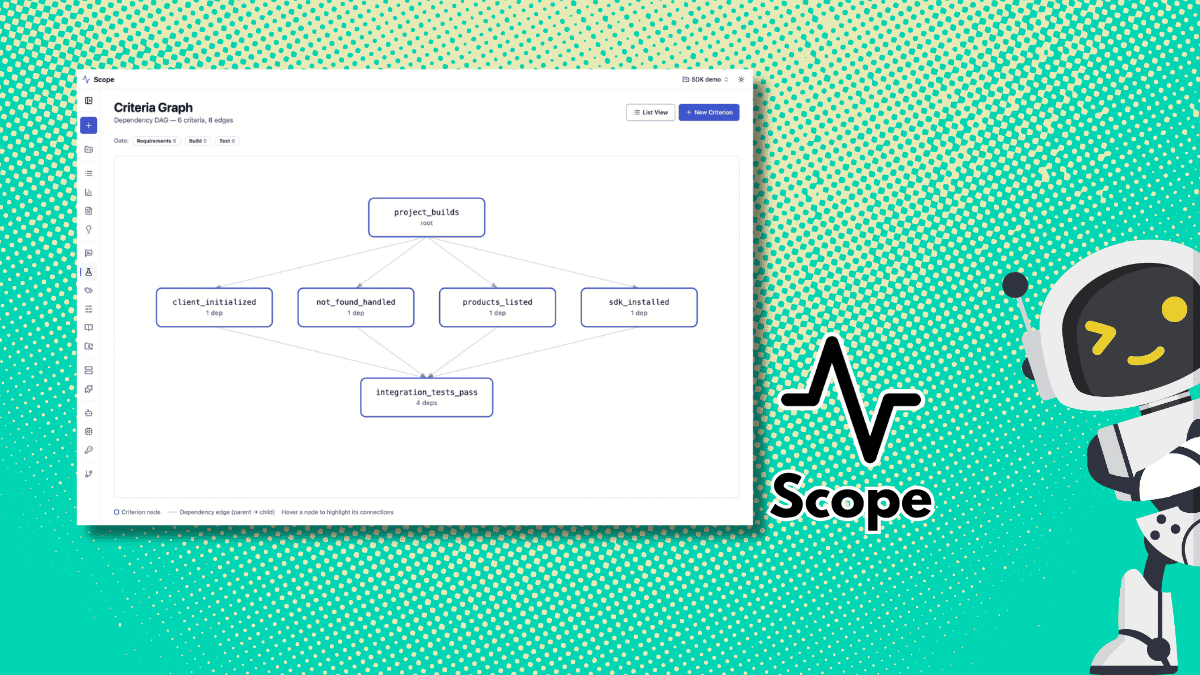
Success is defined through criteria that form a dependency graph. One check can gate another. A simple case is asking an agent for a Node.js server and checking for a GET /health route that returns JSON.

An LLM-based Judge service scores each run against those criteria. Keep in mind that it can make mistakes, and Microsoft says important conclusions still warrant human review.

Each run keeps live logs, generated files, workspace snapshots, and tool calls. A failed criterion can be traced back through those steps. Versioned profiles save the agent, model, skills, MCP servers, and extensions.

You can also swap one, rerun the same task, and compare. Results vary from attempt to attempt, and repeating a task helps separate a recurring problem from a one-off issue.

Then there are the configurable personas that let you set the viewpoint and tone of the simulated user. You can review results in the web portal or use the CLI and REST API to feed them into scripts and pipelines.

Where would you use it?

Docs teams can watch for an instruction that agents miss run after run. Fix the page, then run the scenario again.

SDK maintainers can check whether an agent picks their SDK in the first place. They can also test whether new sample code or a skill changes that.

For CLIs and MCP servers, the traces show where an agent stalled. That can point to a vague tool description or an error message that leaves the agent guessing.

What's the catch?

You can't just sign up and start testing. Scope has no hosted version, so you run it yourself.

A local setup requires these components: Docker with Compose v2, Node 22, pnpm, mkcert, and the GitHub CLI. Microsoft has a local development guide for guiding you through that.

The default worker also calls for an active GitHub Copilot entitlement, and the Judge needs credentials for a model provider. Teams that want a shared deployment can deploy it on Kubernetes with the Helm chart.

Scope's code is on GitHub. Though if you were looking to contribute, you will most likely need to agree to the Microsoft Contributor License Agreement.


Suggested Read 📖: You can use AI to get rid of ads on your smart TV.


from It's FOSS https://ift.tt/g9uQGXc
via IFTTT
Senin, 19 Oktober 2026

CutefishOS is Back With a Vibe-Coded Desktop That Doesn't Use Qt or GTK

cutefishos vibe-coded desktop banner

Anthropic's Fable 5.1 and Opus 5.5 AI models have been used to write the new Cutefish Desktop for CutefishOS, a distro that was in the news a few years ago.

Reion Wong, the creator and developer of CutefishOS, who also runs the project's X account, announced the desktop, showing it off with a demo video and a set of screenshots.

He describes his current workflow as mostly prompting an AI agent, then seeing what it produces.

Is it really built from scratch?

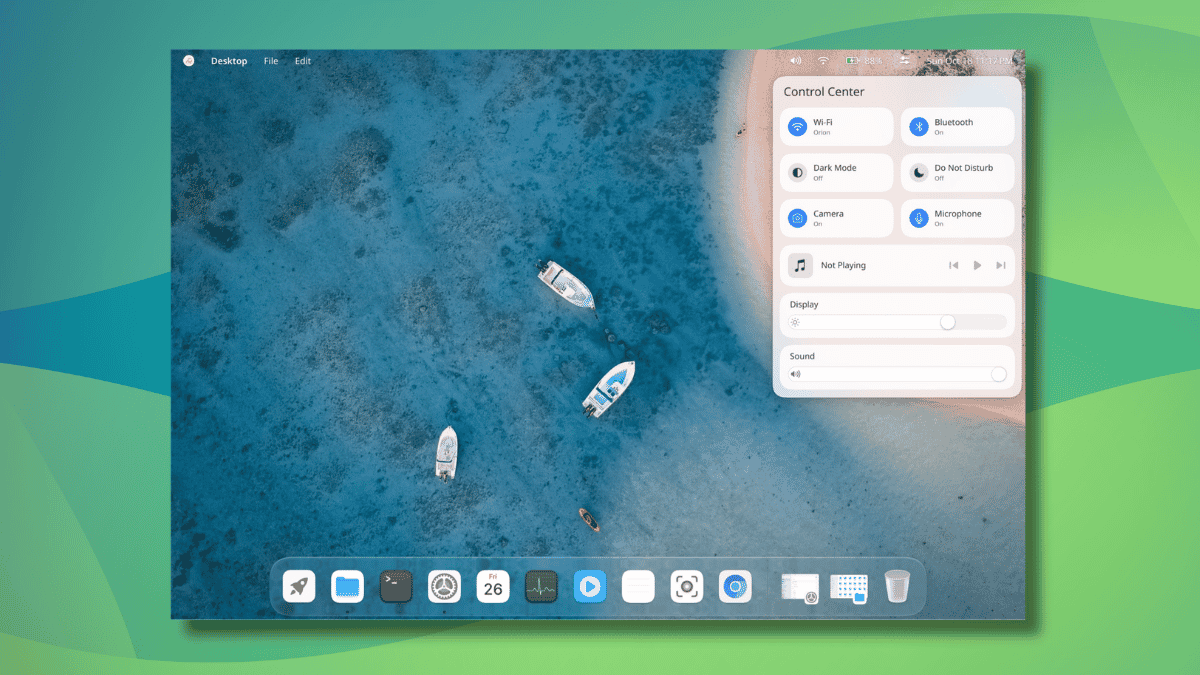
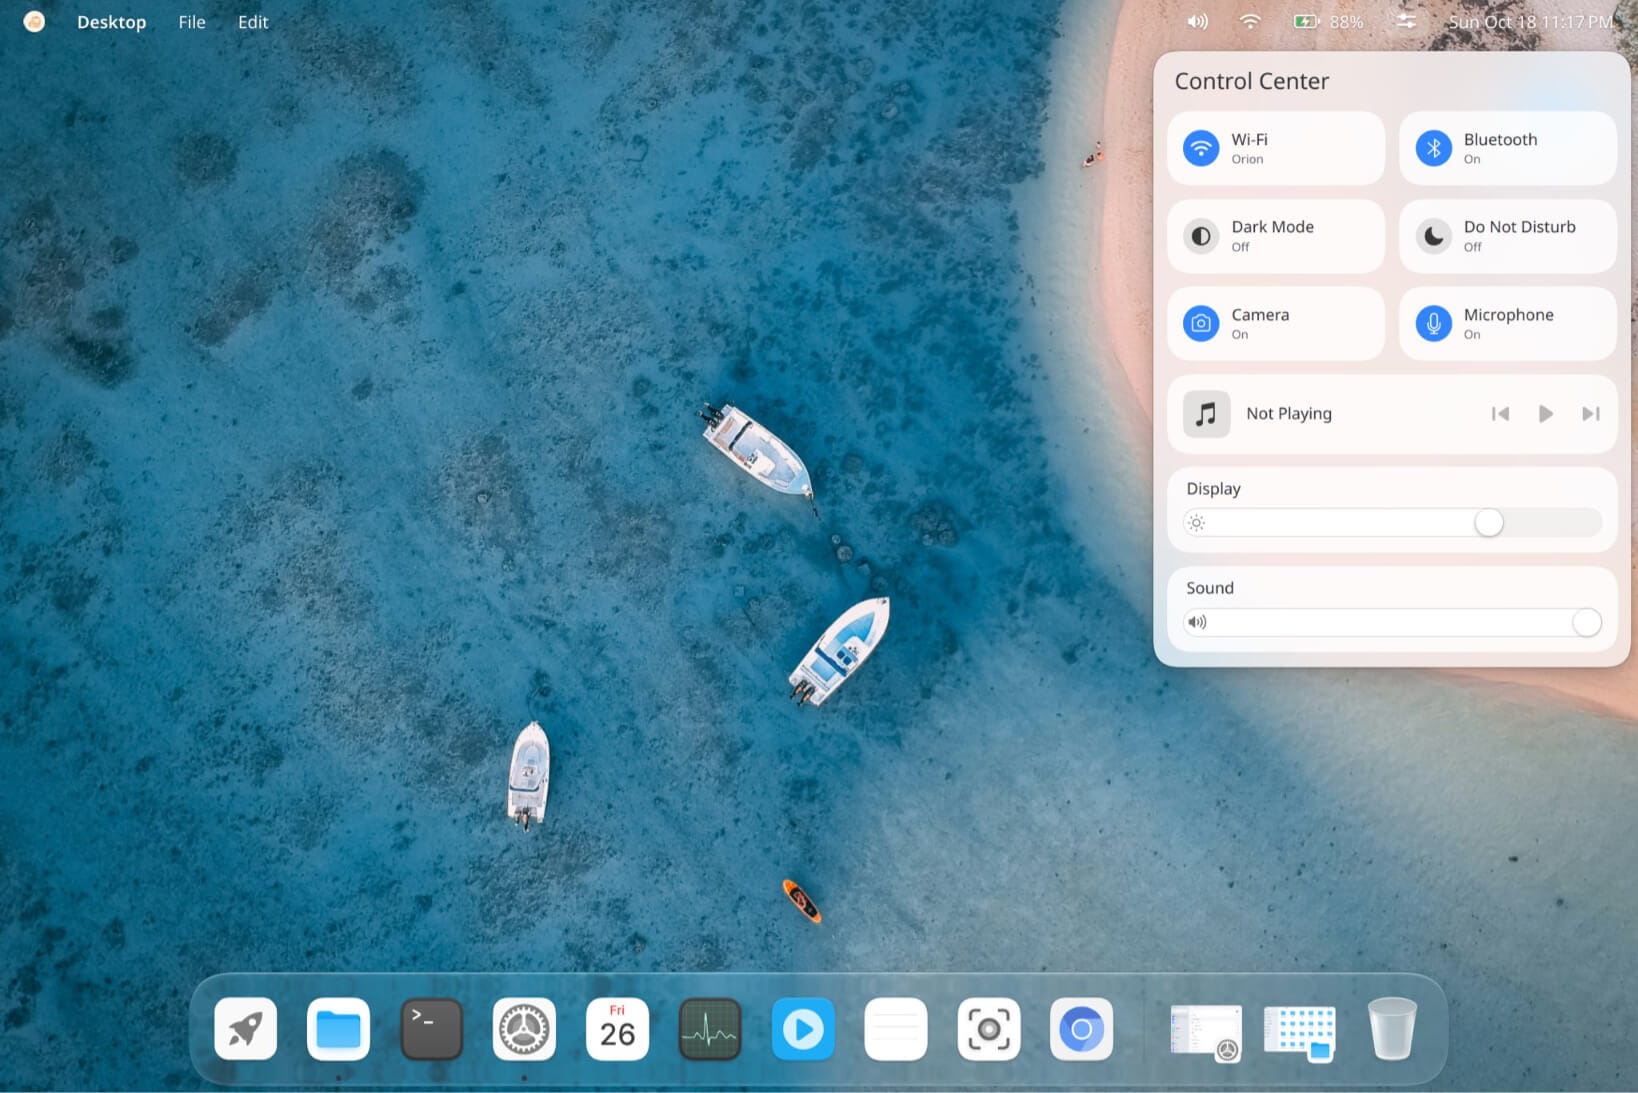
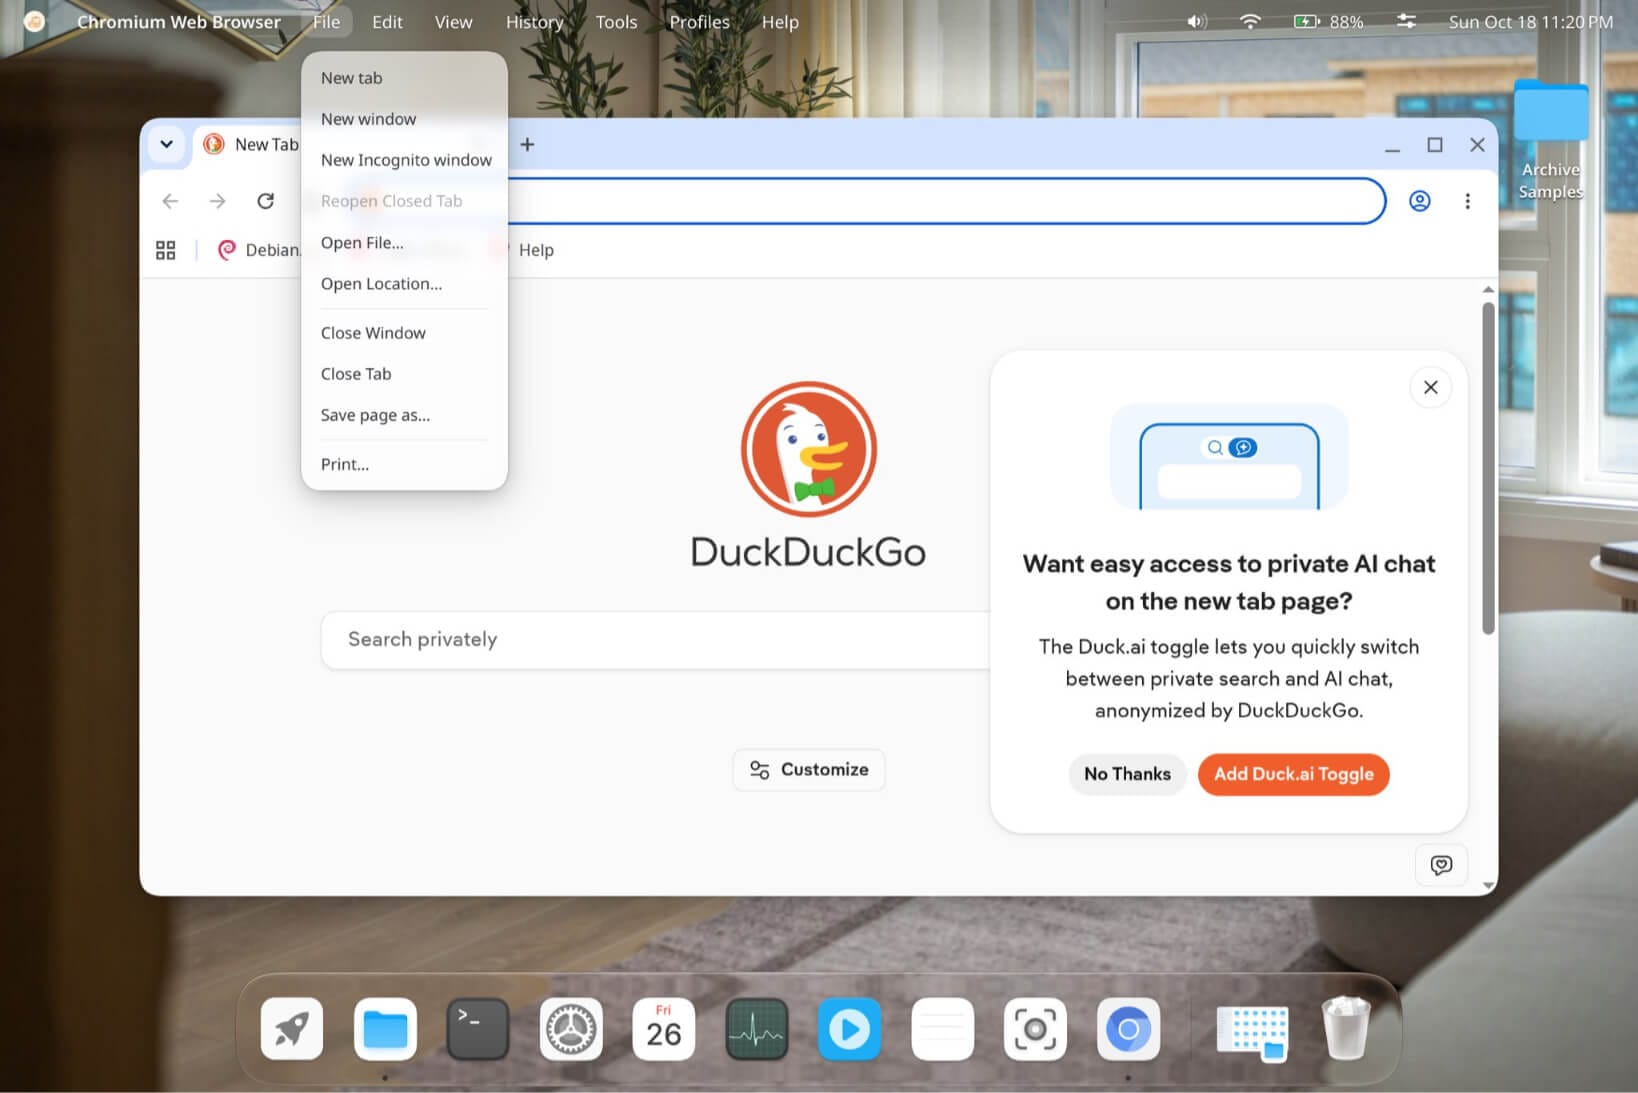
In the video demo above, you can see that the overall look and feel of the interface mimics macOS', with a top bar that houses a Control Center panel, a Notification Center, and standard status widgets.

Control Center holds toggles for Wi-Fi, Bluetooth, dark mode, Do Not Disturb, camera, and microphone, along with media controls and sliders for tweaking the display brightness and sound.

There’s also a configurable Dock that can sit on the left, bottom, or right of the screen, with sliders for its size and glass effect, plus modes like Always show, Always hide, and Smart hide.

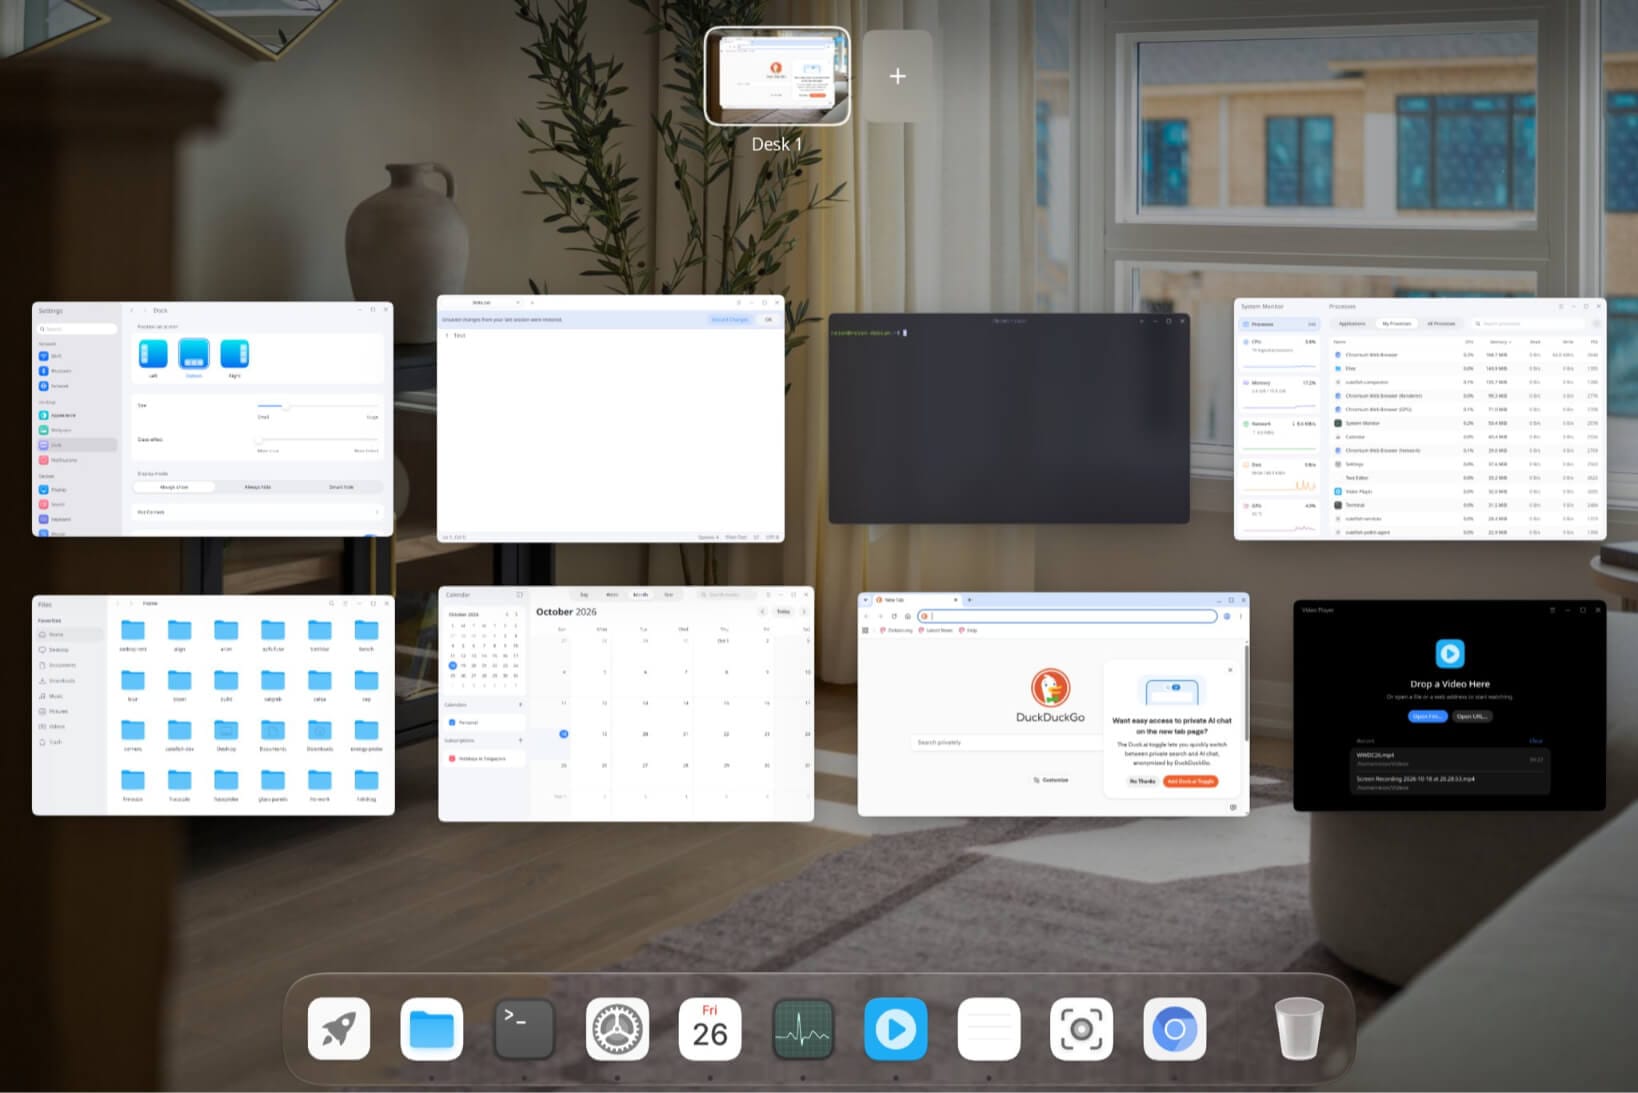
And similar to GNOME, Cutefish Desktop's Overview mode spreads the open windows out on a grid, allowing users to add new workspaces, or "Desks" as the project calls them, from a handy button at the top.

The bundled apps include a file manager, terminal, calendar, system monitor, text editor, video player, screenshot tool, and image viewer that appear to be purpose-built for the new CutefishOS desktop experience.

Chromium, Firefox, KeePassXC, Ghostty, and LibreOffice also show up in the launcher as apps that run on the desktop.

The project says that the whole desktop was rewritten from scratch, including the system apps, and that app launches are very quick. Going further to claim that the compositor and the graphics library are its own.

When someone asked whether the desktop was built on GTK, the project, or rather, Reion, clarified that it doesn't base itself on Qt or GTK.

A look back at CutefishOS

CutefishOS arrived in 2021 as a beta distro based on Debian 11, built around a macOS-inspired desktop called CutefishDE. Back then, it already featured a global app menu in the status bar and a handful of bundled apps.

In 2022, the project’s website stopped loading, and repository activity slowed to almost nothing. A Redditor then started recruiting people for a community fork. The fork plan was dropped after the project’s GitHub said it was back and that a new website was coming.

If you were looking to test the new desktop today, know that no release date has been given. When an X user said they could not wait to try the demo, the project replied that it would take some time before they could test.

Go digging through the project’s GitHub page, and you will find that no dedicated repository for the new desktop is listed. Going by where Reion has been developing CutefishOS so far, that is the place to keep an eye out for the new code.


Suggested Read 📖: This is not the only vibe-coded desktop around; Starling is another implementation that might interest you.


from It's FOSS https://ift.tt/B2wM9rG
via IFTTT
People Are Using AI to Get Rid of Smart TV Ads and Make Their TVs Faster

debloat smart tvs with AI

Last week, we saw a wave of developers determined to reverse engineer everything with AI. This week, there's a new wave, and to be honest, I like this one better.

Some people have found an unusual way of using AI for something that actually matters to them. They are making their smart TVs usable again by stripping the operating system of ads and junk.

If you own a budget Android TV, you know the drill. You switch it on, wait for the home screen to load, scroll past a sponsored banner, and only then reach the app you wanted. People are now asking Claude to fix that for them.

It started with a tweet

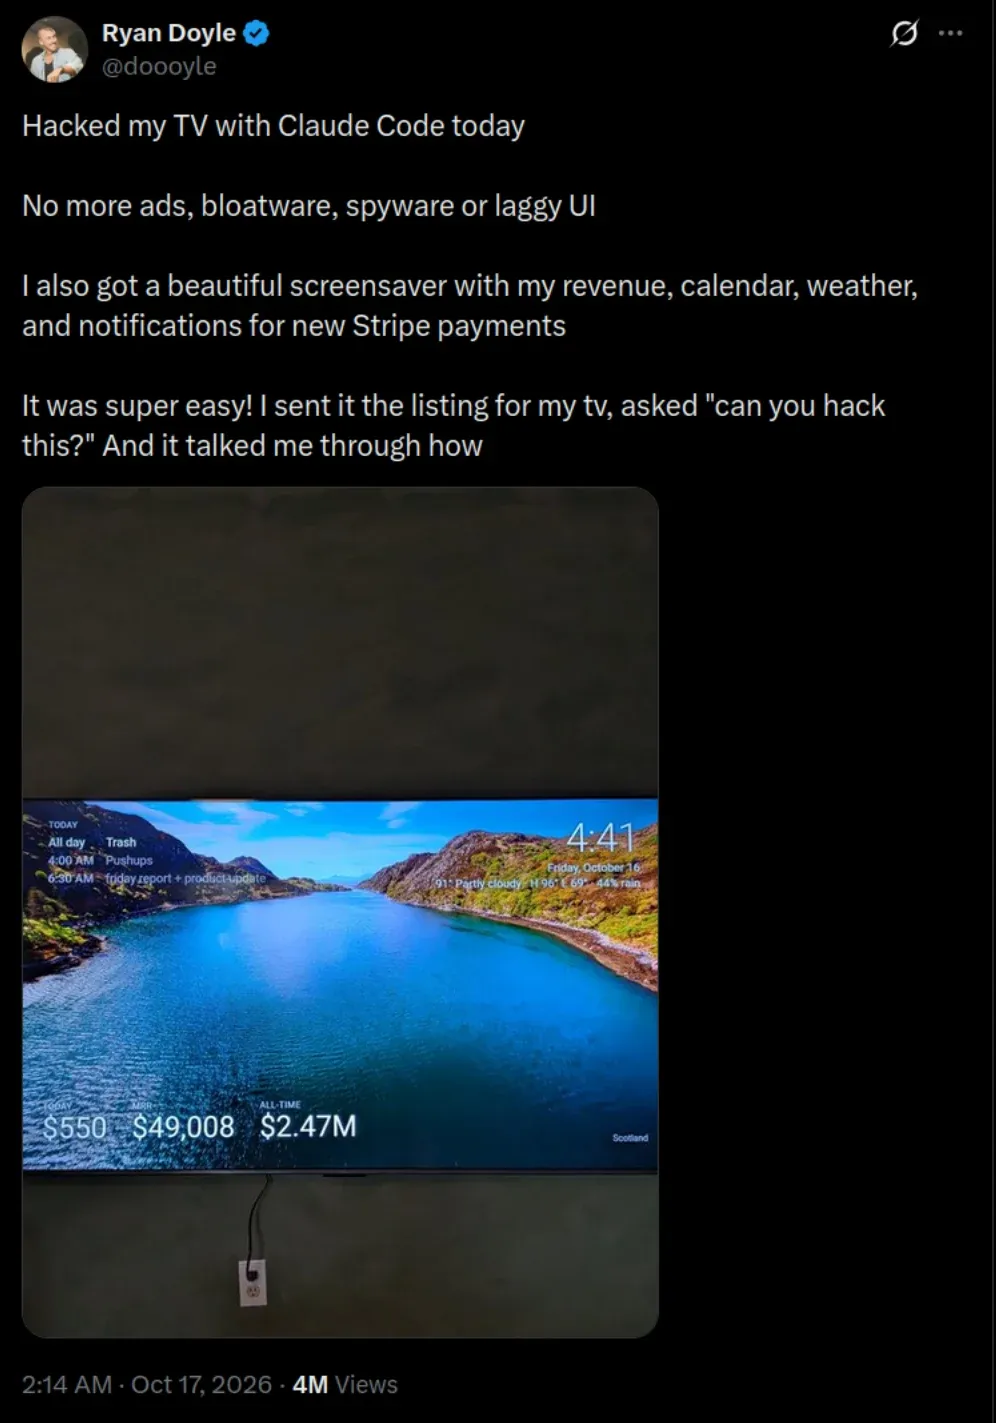
It all started with Ryan Doyle's tweet where he used Claude to clean up his smart TV.

Ryan's tweet telling people that he used Claude to debloat his TV

He then followed up with how much faster the TV had become after the cleanup.

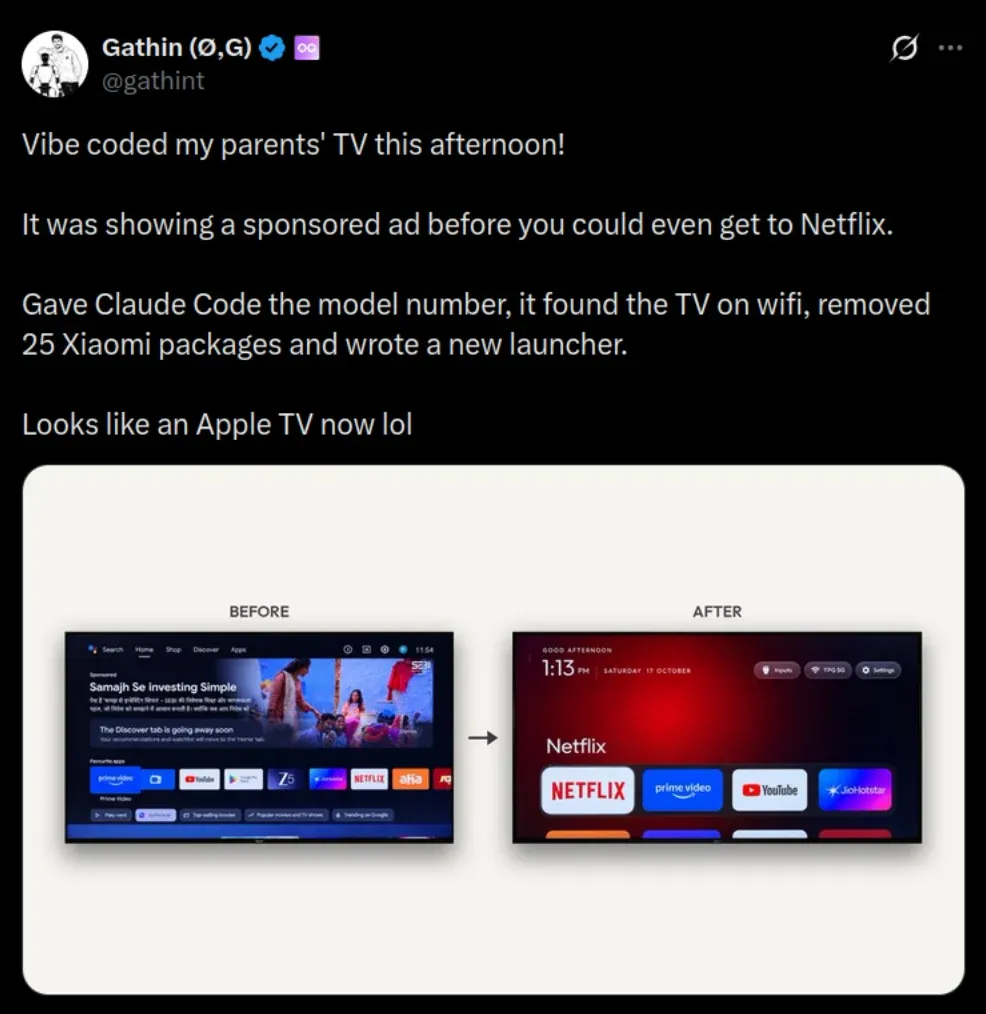
Soon, someone else did the same. "Gathin" went a step further and put everything in a GitHub repo called tv-vibehack. It has the prompt, a custom launcher, and a list of gotchas he ran into.

Vibe coding smart TV with claude

According to the README, it began as an afternoon fixing his parents' Xiaomi Mi TV, which showed them an advert before they could even reach Netflix. The repo is MIT licensed and has crossed 1,300 stars and 146 forks at the time of writing.

How does it all work?

There's no magic here. Android TV has the same Android Debug Bridge (ADB) as your Android phone, and Claude simply does the changes for you.

You enable Developer Options on the TV by going to Settings -> Device Preferences -> About and pressing OK on Build seven times. Then you turn on USB debugging (or wireless debugging, if your TV has it). Some TVs,, like Xiaomi, don't show a wireless debugging toggle at all, but USB debugging alone opens network ADB on port 5555.

Next, you run Claude Code or the Claude desktop app on a computer connected to the same Wi-Fi network. You ask it to connect to the TV's IP address and suggest which non-essential apps can go. Some people use Codex or other coding agents too, but the approach is the same.

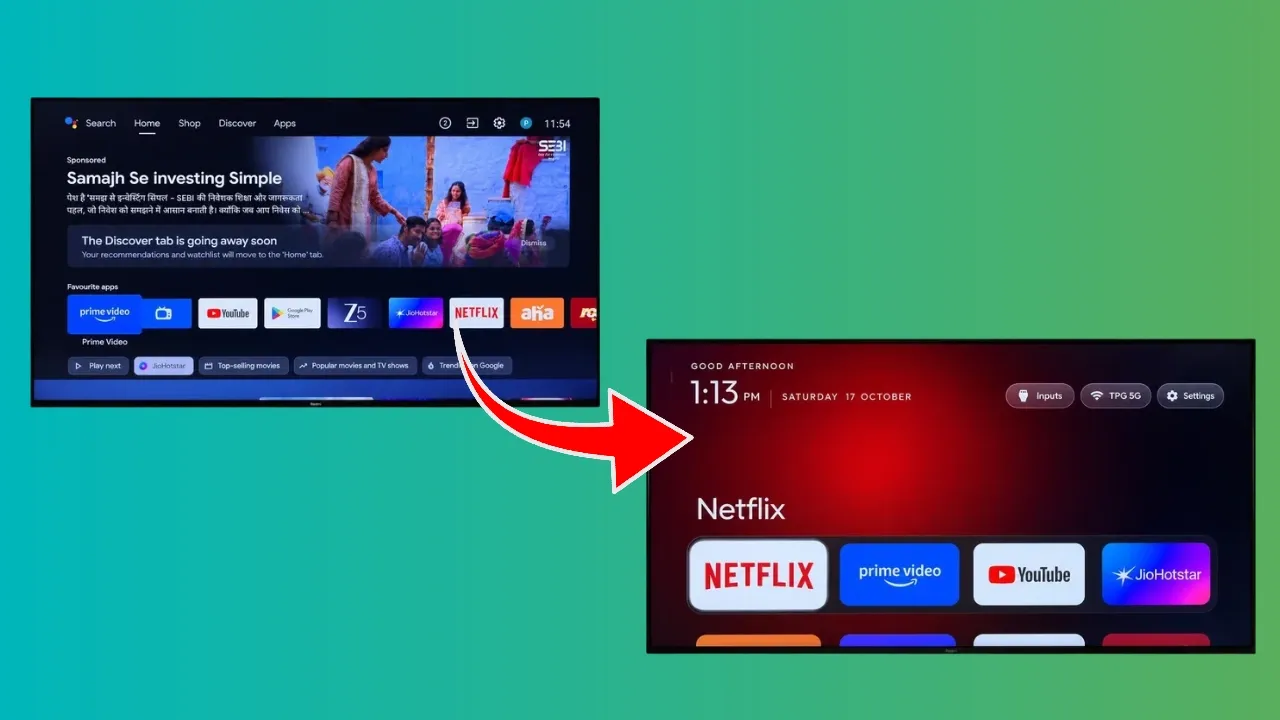
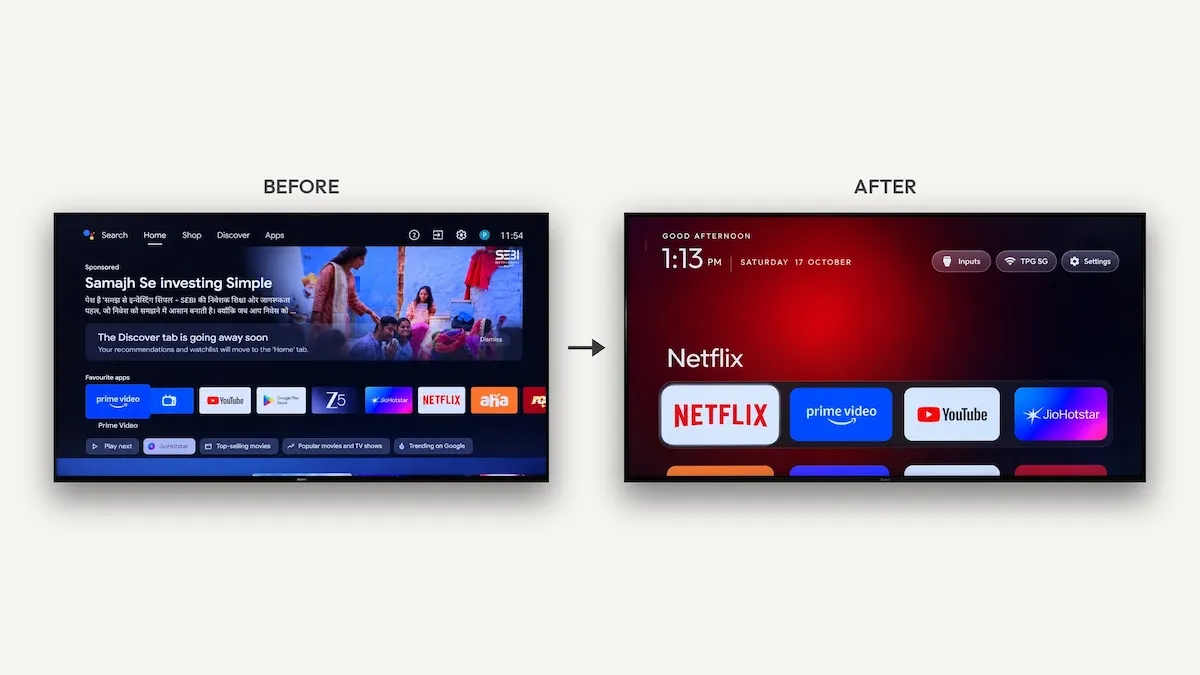
Stock TV vs debloated TV

Almost all the working examples I came across follow the same pattern. The target is Android TV or Google TV, which covers Sony, TCL, Xiaomi, Hisense, OnePlus, etc.

Samsung (Tizen), LG (webOS) and Roku are run entirely different systems so the debug trick doesn't work here. Perhaps someone will find a way out here as well. Amazon Fire TV needs extra care (more on that later).

Claude lists the installed packages and disables (not uninstalls) the ads, sponsored rows, telemetry and preloaded bloat with pm disable-user. Many people also install a minimal custom launcher in place of the ad-filled stock home screen and tone down the animations.

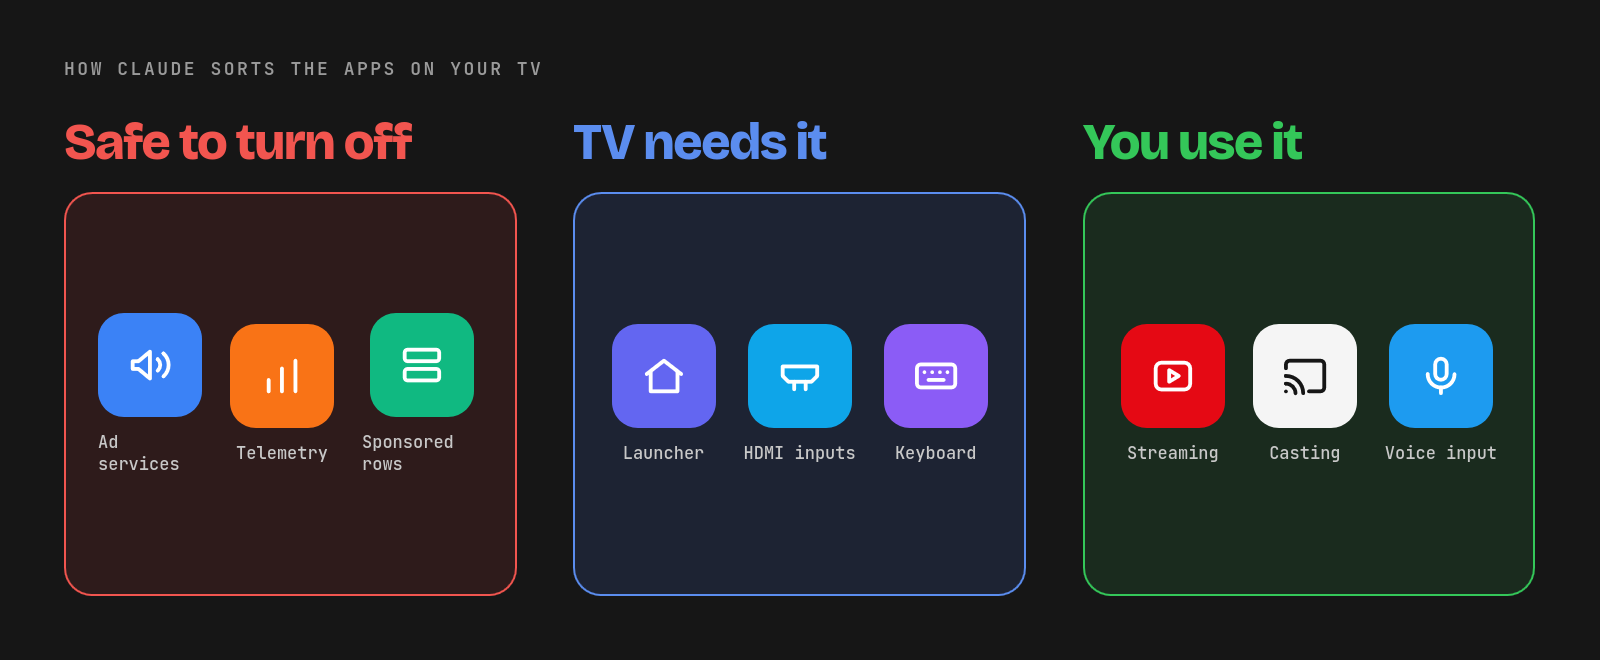
How claude turns the app off in a smart TV

Everything is meant to be reversible. And it should be. Good prompts insist on a backup of the package list first and ask before touching anything important, such as HDMI inputs, firmware updates or the keyboard. The tv-vibehack prompt, for example, quizzes you on which streaming apps you use and whether to keep the voice assistant, Chromecast and updates.e

As per the README, the first run on a 1 GB Mi TV took an afternoon. With the repo as context, people report getting it done in about fifteen minutes.

Gotchas people point out

People who have done it have shared a few lessons, and they are worth reading before you let an AI agent loose on your TV.

The first and biggest one: disable, don't uninstall. Uninstalling system packages is the way to brick the Home button or lose HDMI input switching. Even the order matters. tv-vibehack warns that if you disable the stock launcher before the new one is installed, the Home button lands you on a factory test app.

Turn off USB or wireless debugging when you are done. You don't want an open ADB port sitting on your home network.

Many of the cheap Android TVs ship with only 1 to 2 GB of RAM, so how much faster your TV gets depends on what it shipped with. That's also why the tv-vibehack launcher skips blur, video and background services.

And then there's Claude itself. Some people reported that some sessions refuse when they tried with "hack my TV". You are likely to get better results by sharing the model number and package list first and asking it to clean up ads and speed things up.

Don't disable everything just because you can

In my opinion, you should not disable every service just for the sake of it. Ads and telemetry, sure, get rid of them. But not every background service is bloat.

Disabling voice input and screencast may make the TV a bit faster. But it also takes away the convenience of searching with your voice or casting a YouTube video from your phone to the big screen. If other people in the house use the TV, they may not thank you for that.

The same goes for firmware updates. Most debloat lists turn off the manufacturer's update service, which also means you stop getting fixes. Decide what you actually use before you let AI decide what to cut.

More repos to make your smart TV dumb

Since it became a trend, more GitHub repos have popped up to make the smart TV dumb again. One of them is dumbtv, and it covers a few gaps tv-vibehack leaves.

tv-vibehack doesn't support Amazon Fire TV, while dumbtv is built for it. It has been tested on a Fire TV Edition television running Fire OS 7.7.1.7 (based on Android 9).

It also goes further than just disabling apps. It disables around 65 packages, including Amazon's ACR (screen fingerprinting), ad ID and watch-time analytics. It runs personalDNSfilter on the TV to block Amazon telemetry and update servers, and replaces the home screen with its own 41 KB launcher that has no permissions at all.

This repo is written for AI agents as much as for humans as it ships an AGENTS.md, a CLAUDE.md, an llms.txt and a skill file, so you can point Claude at the repo and let it follow the steps. Still, read the skills or have it vetted on your own.

Taking back the TV you paid for

This is the real way real people are using AI. Finally some good use of AI to take back control of a device you already paid for, and yet see ads anyway.

If you have an old Android TV that is pathetically slow, this might be worth a weekend afternoon. Just mind to disable instead of uninstalling, and keep the features your family actually uses.

Would you use something like this? Comment section is yours.


from It's FOSS https://ift.tt/ElYBTJG
via IFTTT
Minggu, 18 Oktober 2026

Linux Kernel 7.3 Release is Good News For Gamers Short on VRAM

linux kernel 7.3 release banner

A new kernel release is here about two months after Linux 7.2, and its biggest draw is performance.

Filesystem speedups, scheduler work for gaming, and lower latency for real-time workloads lead the way, with hardware support and a few other smaller changes topping it off.

Of course no new kernel release, even a point release, is complete without a word from Linus Torvalds:

...nothing very special seems to have happened this last week, so as expected the final 7.3 is out, and thus tomorrow the merge window for 7.4 opens. Except I'm on my annual family vacation, so instead of merging anything first thing in the morning, I'll spend most of the day on a boat and under water. I'll get back to merging in the afternoon, but I expect my schedule to be a bit unusual for a while.

If you are wondering about "under water", that's probably Torvalds referring to scuba diving, one of his rare non-nerdy passions.

Linux 7.3: What's New?

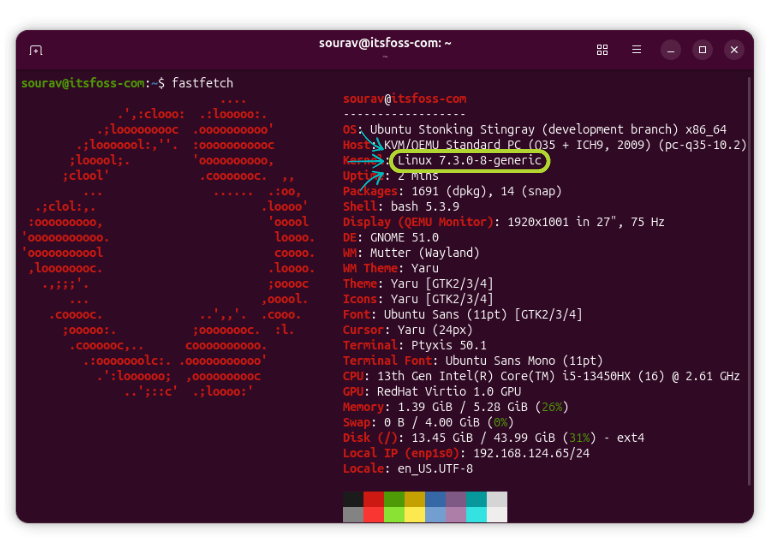
linux 7.3 fastfetch output on ubuntu

AMD's HSMP driver now supports protocol v7, which Zen 6 Family 1Ah Model 80H processors rely on. The CPU manufacturer has been busy laying the groundwork for those chips that are set for a January 2027 launch.

The PMF driver also picks up support for the same family and adds a new ioctl interface that delivers device metrics.

Not everything is Zen 6 groundwork, though. Ryzen AI Halo mini PC owners can now control the lighting of their device when using the kernel through the new amd_halo_led driver.

Before this, toggling the LEDs only used to work via AMD's Debian-based distro for the device, the Ryzen AI Developer Platform.

If you like tinkering with CPU power behavior, the amd-pstate driver has a change for you.

The opt-in Dynamic EPP (Energy Performance Preference) feature lets the kernel adjust the preference on its own, and it used to be only a system-wide switch. You can now turn it on per CPU core by choosing the "dynamic" preference under the powersave governor.

Older Radeon cards get better recovery from GPU hangs too. Valve's Timur Kristóf reworked the reset so it only resets the GFX block, the part of the GPU that handles graphics work, and leaves graphics memory alone.

Another Valve engineer, Natalie Vock, has been working on better gaming performance for cards that run short on VRAM, and the first piece of that work is in this Linux release.

Basically, when video memory fills up, the kernel can now move less important data out to system RAM to make room for what a game needs.

With the full set of patches, Indiana Jones and the Great Circle asked for 9GB on an 8GB card and still ran well enough to play. Her full set already ships in SteamOS, and the rest of it is still on its way to Linux.

Then there's the system memory management tweak, where ZTE engineers found that a lookup used for KSM, the feature that merges identical memory pages, could hold a lock for hundreds of milliseconds and freeze apps under memory pressure.

Their fix brought down the worst case in a stress test from 705ms to under 2ms.

Xiaomi's Wenchao Hao tackled a similar lock slowdown in zsmalloc, which zRAM and Zswap use to store compressed memory, and saw gains of up to 1.83x on a Raspberry Pi 4B and 1.4x on a 20-core Intel system.

We wrap this up with a few other notable changes:

  • RISC-V gains support for eleven newer ISA extensions, and it now uses UEFI runtime services for handling restarts and power-offs.
  • Apple's M3 Pro, Max, and Ultra chips get initial support for booting Linux.
  • Intel's Starfire, a space-grade chip based on Panther Lake, gets its first Linux changes.
  • Logitech's logitech-hidpp driver enables remapping of buttons on newer, enthusiast-class mice and keyboards through HID++ 2.0.
  • The hid-steam driver now supports the 2026 Steam Controller.
  • Users of Lenovo ThinkPads with USB-C Restricted Mode Security functionality can now take advantage of it on Linux.

For details on the storage, scheduler, and real-time latency improvements, you can refer to our preview coverage.

Can't wait to get started?

This year's Ubuntu interim release, Ubuntu 26.10, is the most straightforward way to get on the Linux 7.3 release. If you don't prefer that distro, then you could always wait for the upgrade to arrive on Fedora Workstation and on Arch Linux and its derivatives.

You could also install the latest mainline Linux kernel on Ubuntu if you don't mind risking your setup. But remember, there's a possibility you could lose data, so back it all up before going down that path.


from It's FOSS https://ift.tt/lXJpUmj
via IFTTT
Sabtu, 17 Oktober 2026

Not Every Open Source OS Needs to Be Based on Linux, and These Six Aren’t

open source os list penguin-themed banner

Anyone who wants a break from Linux is usually told to try another distro. That advice, while good, leaves out those who want a break from Linux itself.

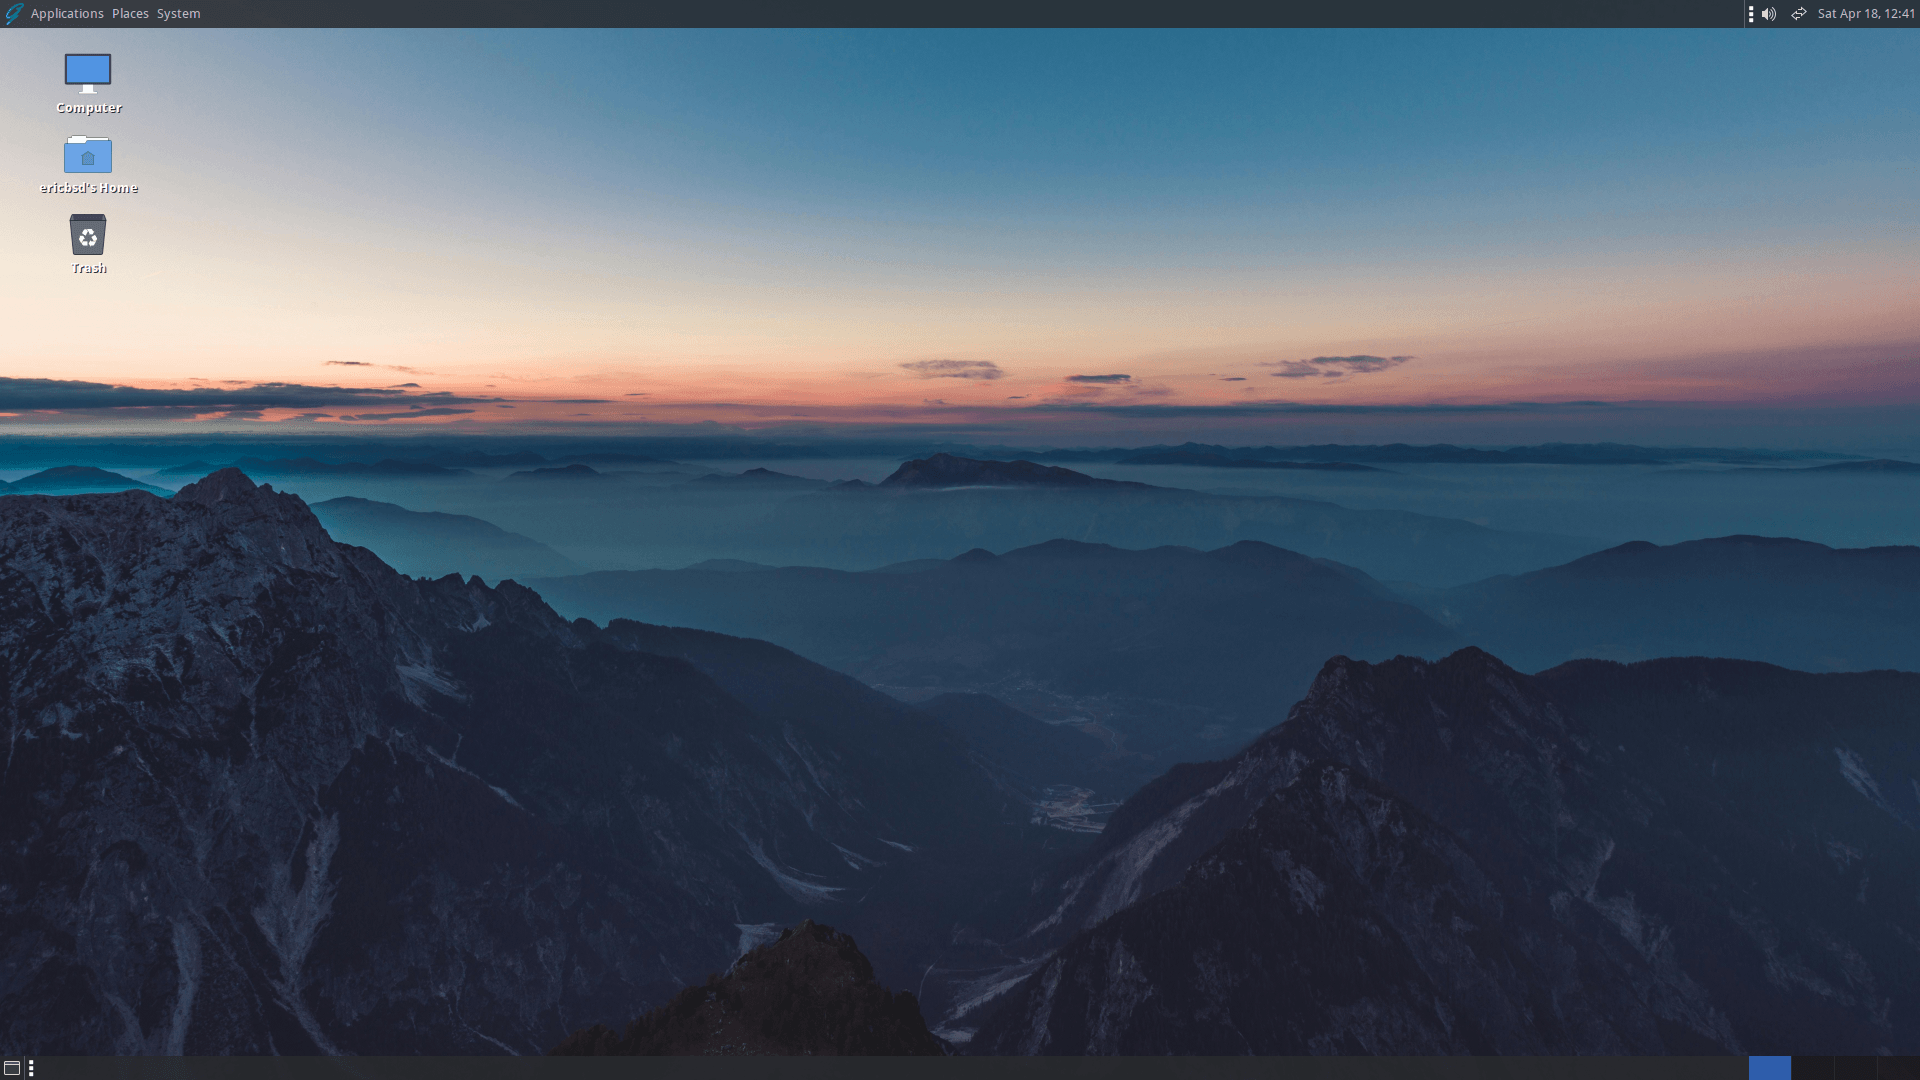
Every system listed below is open source and not powered by Linux. Each has an ISO or installer you can boot today, and many of the picks can even run Linux applications.

Think of it as a list of operating systems that are friends with Tux🐧 but not friendly enough to call him inside for a cup of tea.

📋
This list is not ranked. The order moves from the BSDs to the desktop-first systems and ends with the two newest kernels.

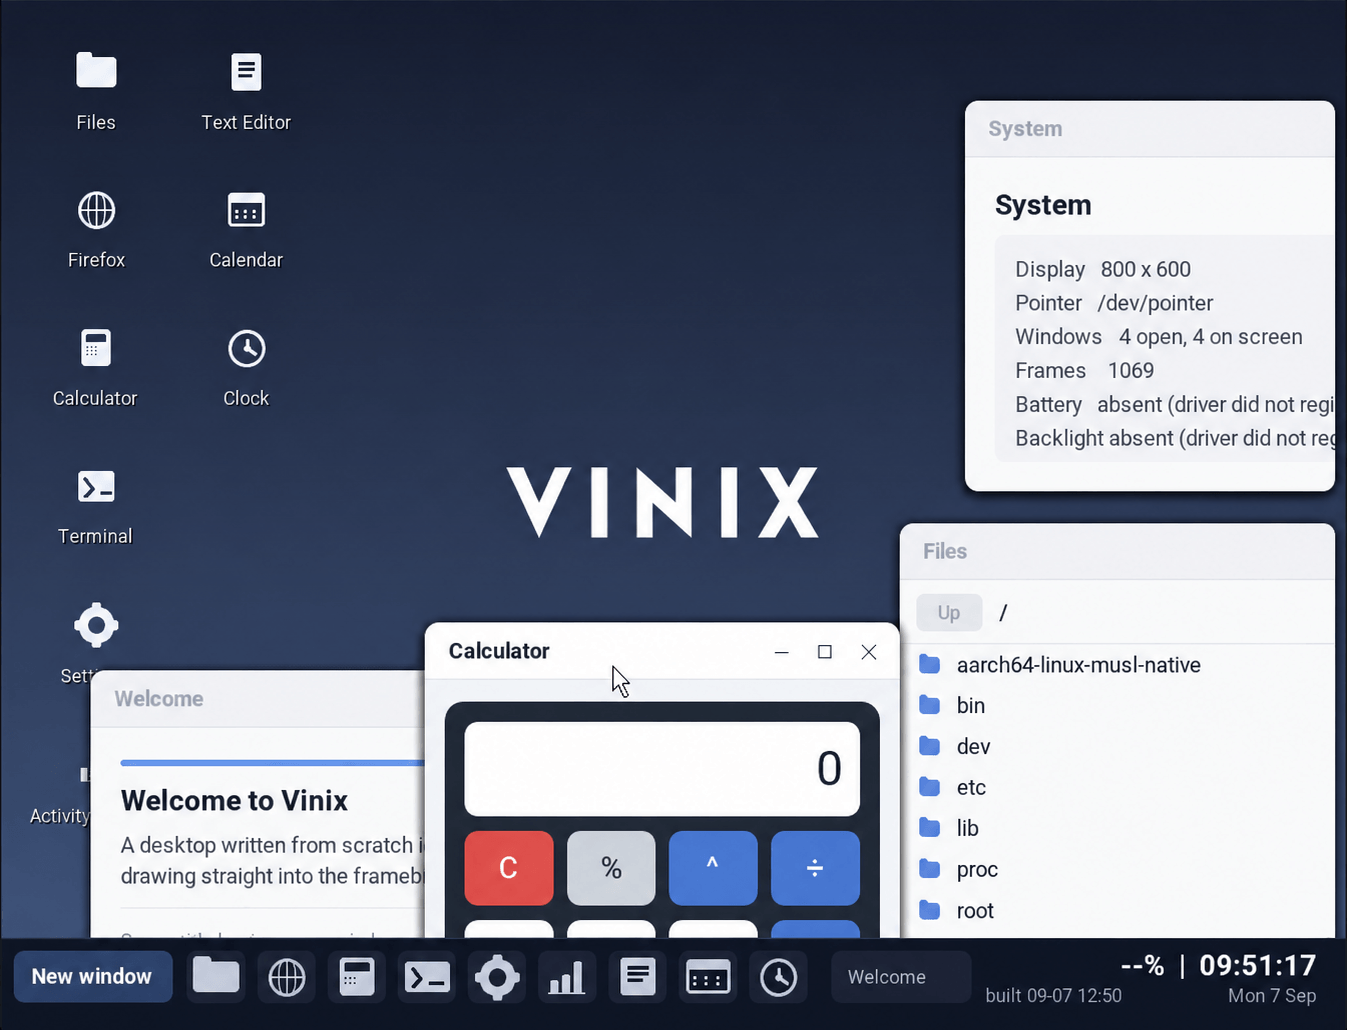
1. Vinix

vinix

If you own an Apple Silicon MacBook and want a system that is neither macOS nor a Linux distribution, Vinix is aimed at you. Only the original M1 is supported today, and Alexander Medvednikov, the author of V, maintains the project.

The kernel is monolithic and written mostly in V, while part of it is C and assembly. Because memory is managed by hand, no garbage collector can interrupt a system call, and the security model borrows certain concepts from OpenBSD.

On ARM64, it runs Alpine Linux binaries natively, and pkg installs packages from Alpine's aarch64 repositories. ISOs for both x86-64 and ARM64 are available for virtual machine use.

⭐
A good pick if you enjoy poking at experimental kernels.

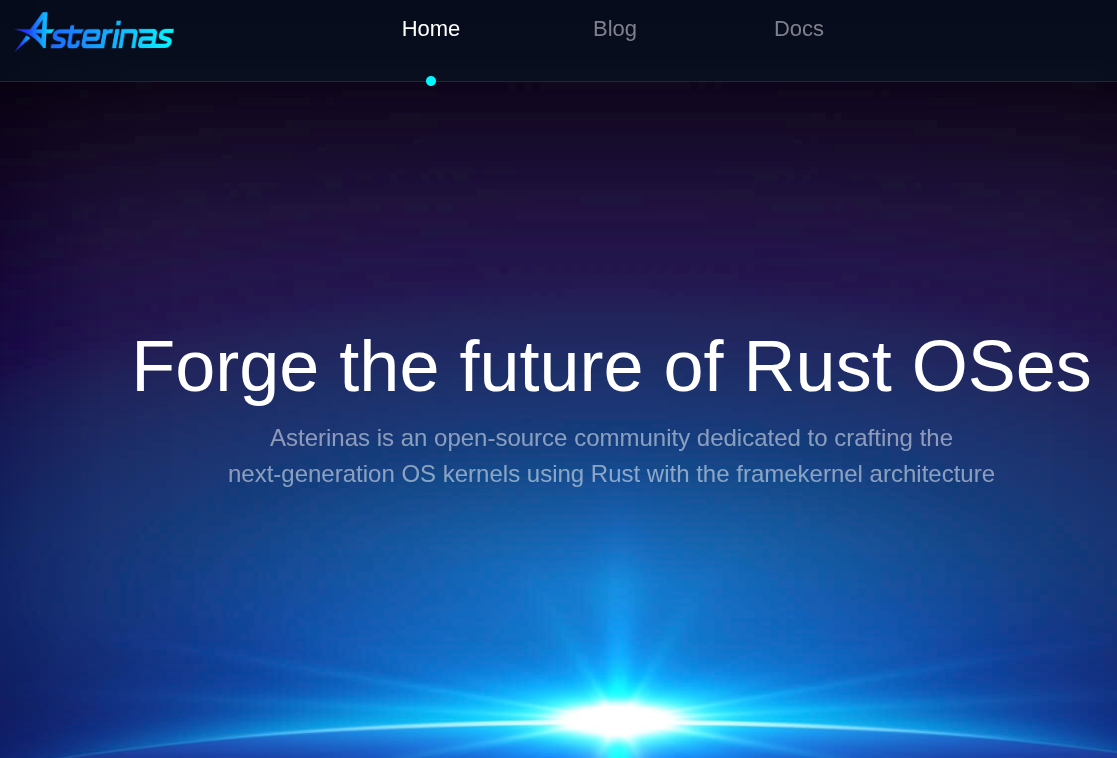
2. Asterina NixOS

asterinas webpage

Trying Asterinas NixOS means setting up a NixOS system and finding a Rust kernel where Linux should be. Asterinas is that kernel, and because it implements Linux's system call interface, apps for the Linux platform run on it.

The distribution is configured through Nix like regular NixOS, and unsafe Rust is allowed only inside a small framework called OSTD, while the rest of the kernel, along with its drivers, is safe Rust.

x86_64 is the fully supported platform, and ARM64 and RISC-V sit one tier below it. The project says the distro is not ready for production use and aims the installer ISO on GitHub at early adopters and enthusiasts.

⭐
A good pick if you follow the implementation of Rust in operating systems.

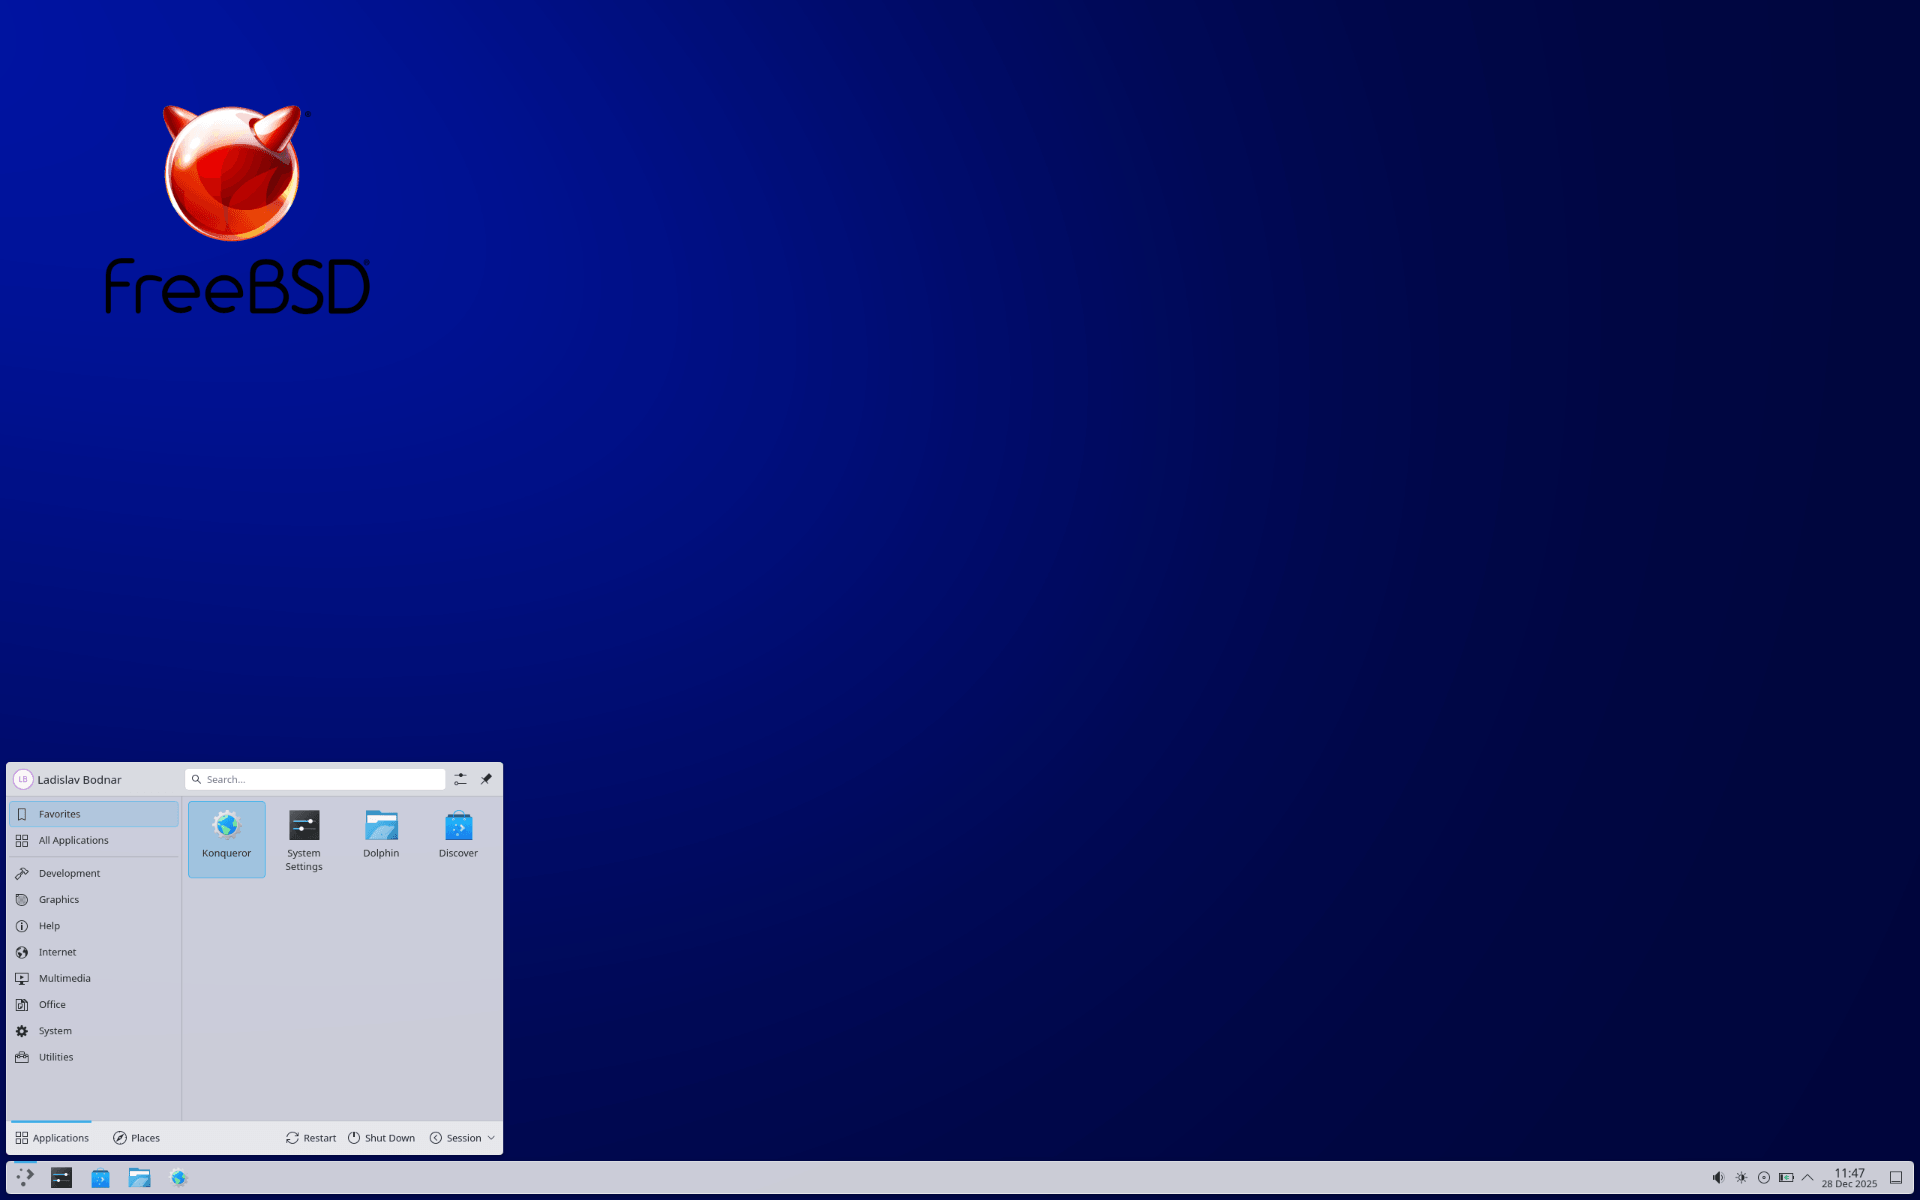
3. FreeBSD

freebsd
Source: Distrowatch

FreeBSD is a complete operating system derived from BSD, the Unix version developed at the University of California, Berkeley. A large community maintains it, and its license lets companies keep their own changes private.

ZFS, jails, and a hypervisor sit at the center of what it offers. OpenZFS is built into the base system, and boot environments let you roll back a bad update by snapshotting the system first.

Its recent release, FreeBSD 15.1, came out earlier this year, and the OS runs on hardware platforms like AMD64, AArch64, Armv7, PowerPC, and RISC-V.

⭐
A good pick if you run servers, storage, or networking gear.

4. GhostBSD

ghostbsd

GhostBSD is FreeBSD with the desktop work already done. The project pairs a FreeBSD base with the MATE desktop and offers a set of applications that make users feel familiar with using it.

The name started as shorthand for GNOME hosted by FreeBSD. MATE, the desktop it ships today, is a continuation of GNOME 2, and the old name still fits.

Updates arrive on a slow-rolling schedule, and the project says it values a stable cycle over chasing the newest software the way some Linux distros do. The current release, 26.1-R15.0p2, came out in April on a FreeBSD 15.0 base.

Also good to know is that Linux binary compatibility comes preconfigured, and an installer built on OpenZFS keeps setup approachable for newcomers.

⭐
A good pick if you want FreeBSD as an everyday desktop.

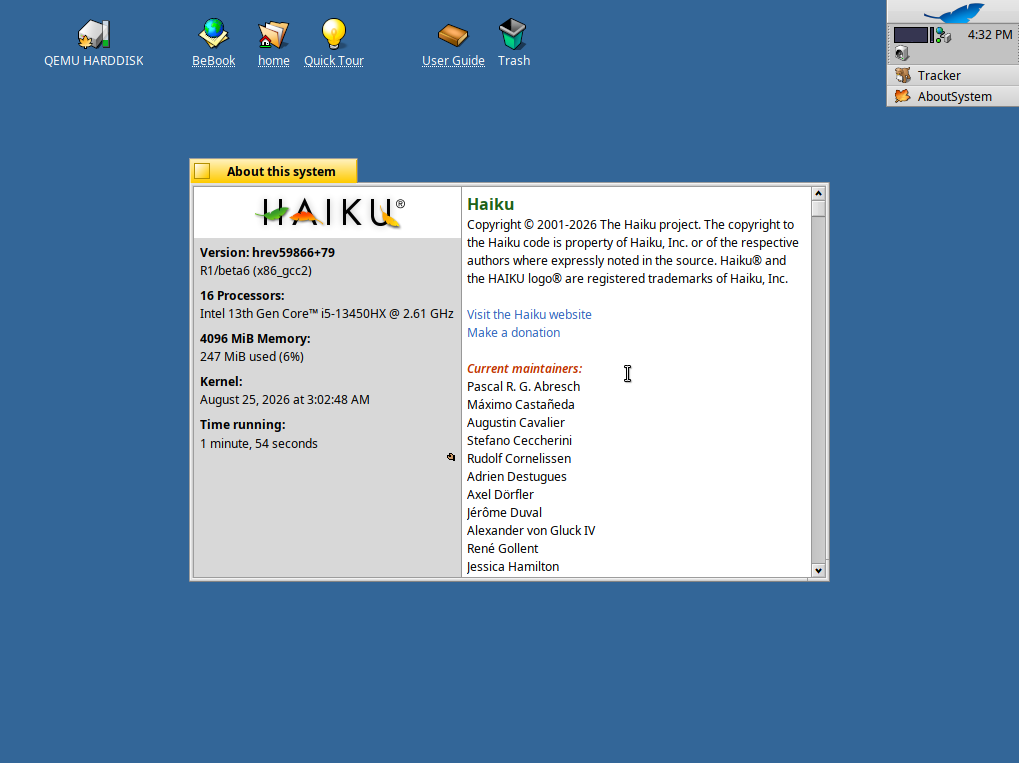
5. Haiku

haiku

Haiku is an open source operating system inspired by BeOS that is aimed at personal computing. The same team writes the kernel and the desktop applications, with the project crediting that approach for the system's consistent interface.

Under that interface sits a kernel built for responsiveness, a system that is multithreaded throughout, and a BFS file system whose indexed metadata lets Tracker, the file manager, run database-style queries across a drive.

Software installs are handled via packages that mount into the system, and earlier states are kept for rolling back botched updates.

⭐
A good pick if you are looking for a uniform desktop experience.

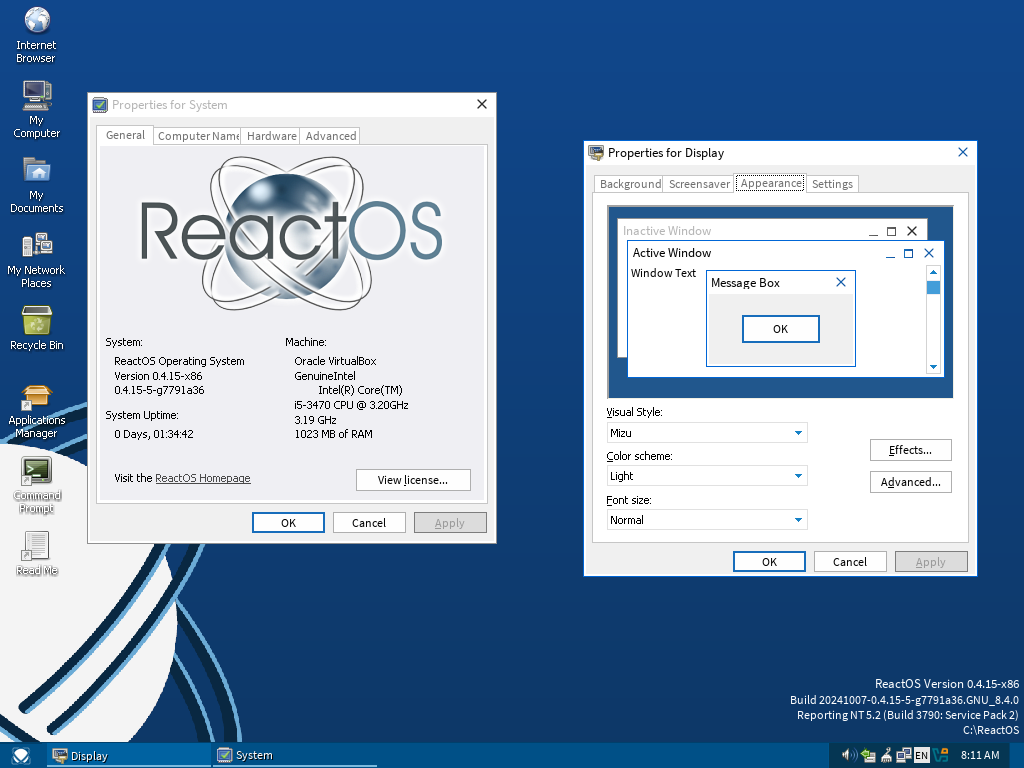
6. ReactOS

reactos

ReactOS comes with a warning label attached because the OS is still considered alpha-level software, and the download page promises nothing about stability, the safety of your files, or whether it would work on your hardware.

Behind the warning is a full operating system with a Windows-style desktop that the project says was written from scratch, while most of its user-mode code is based on Wine, the ubiquitous compatibility layer.

By default, it installs only onto a FAT16 or FAT32 partition, and Btrfs support is experimental.

⭐
A good pick if you want to see how far an open source Windows reimplementation can go.

A suggestion

Try these operating systems in a virtual machine before switching. I say that because it’s a good habit to test out such non-standard pieces of kit before committing to them on your hardware.

First see what works for you. Then see if your workflow and usage habits align with what the OS offers. Once you settle on one, keep it updated so you never miss critical patches.

Air-gapped setups are better protected from such risks, of course.


from It's FOSS https://ift.tt/4sCNv6T
via IFTTT
Jumat, 16 Oktober 2026

Valve’s Steam Client for Linux Goes 64-bit in Beta and Moves Into a Container

steam 64-bit banner

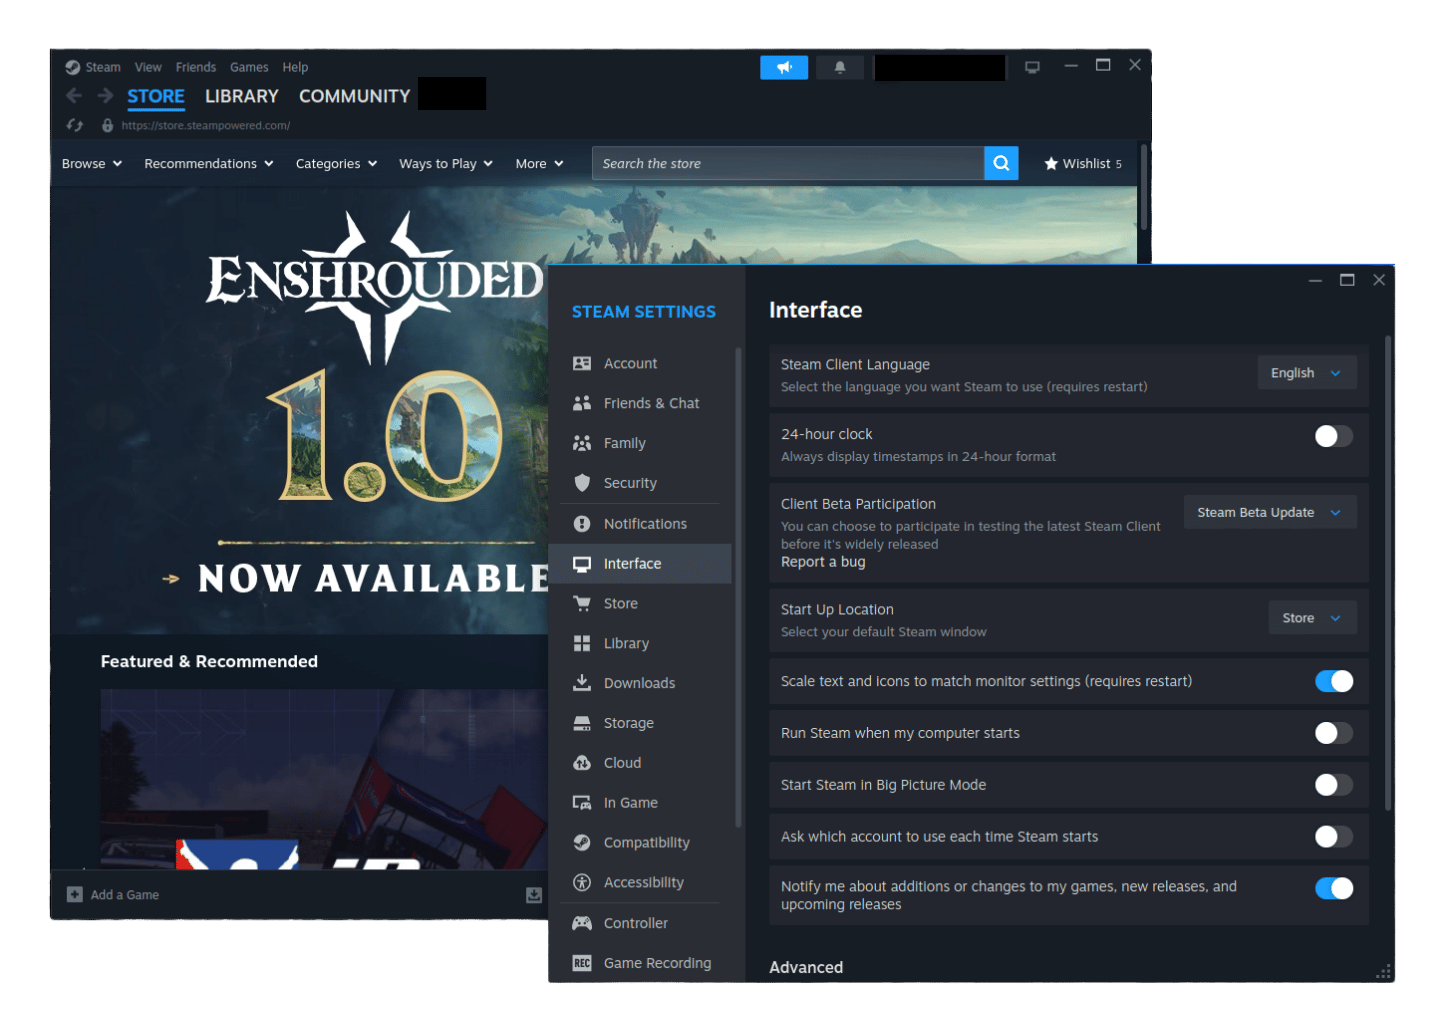
Valve's October 15 Steam Client Beta changes how the Linux client is built and run. It moves the client to a 64-bit build and runs it inside a Steam Runtime container. Alongside that, a fix for the updater window failing to show up is included, as is the new Achievement Sets feature.

According to Valve, the client has run in an older setup that layers Steam Runtime libraries over the ones on the host system. The runtime documentation adds that this only works while the host is newer than the runtime.

Games on Steam can already run in containers, which give an application its own set of libraries rather than blending them with the host's. The tool behind those containers, pressure-vessel, still takes graphics drivers from the host system.

Valve says running the client in a container should make it behave more consistently across distros. Its games already run on the same technology.

steam rt3 linux beta client

The release notes for the beta client do not name the container, but its runtime release notes tie the 64-bit client to one called steamrt3c. The README describes it as a variant of the sniper runtime made for use inside the Steam client.

The groundwork for this can be traced back to March, when Valve put the container and the early 64-bit client out as the Linux SteamRT3 Beta.

And don't assume that opting for a 64-bit client removes the need for 32-bit libraries.

The requirements for the beta client still call for both 32-bit and 64-bit versions of the required libraries and graphics drivers on x86_64 systems.

They also list 64-bit-only setups as unsupported. The steamrt3c README from earlier notes that its containers ship i386 libraries for compatibility with older software.

Test it now

I switched to the beta on Ubuntu 26.04 LTS, and it only took me four steps. If Steam is not already on your system, you need to get the official DEB package for the client and install it.

Next, follow these steps. 👇

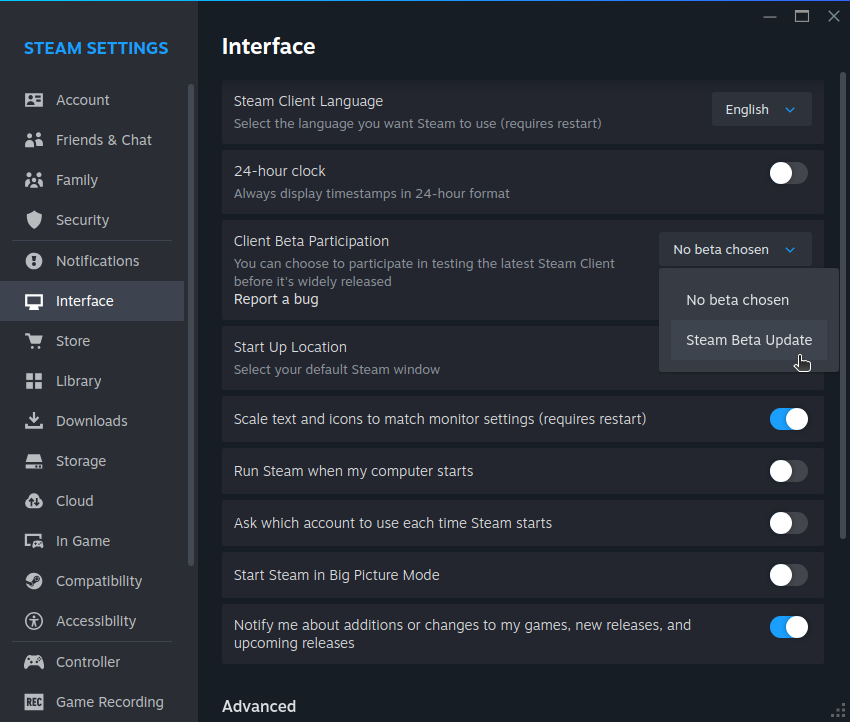
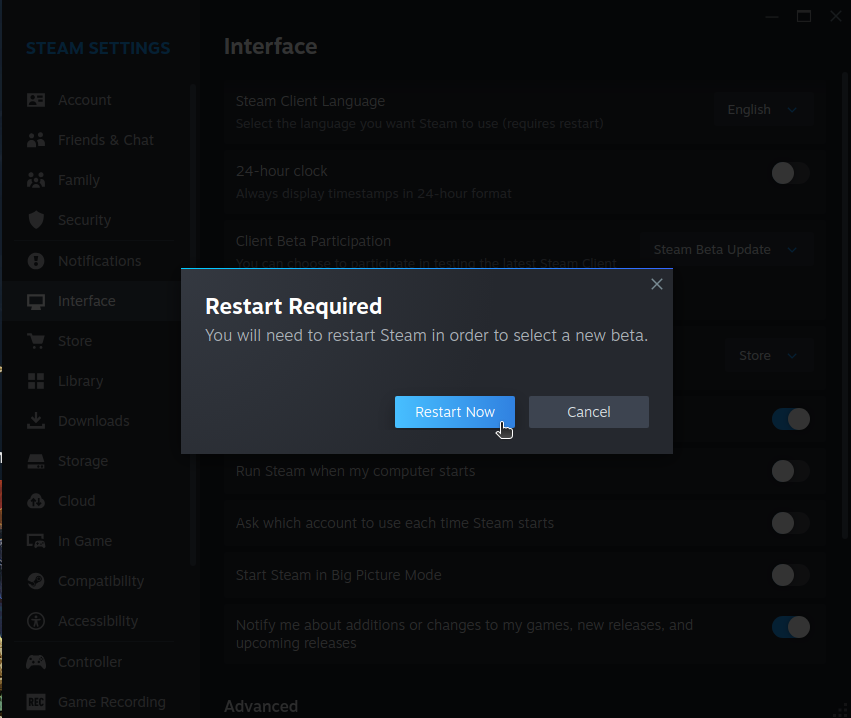
  1. Open Steam, click Steam at the top left, and choose Settings.
  2. Go into the Interface tab and find Client Beta Participation.
  3. Open the dropdown and select Steam Beta Update.
  4. Click Restart Now when Steam asks you to restart.

That is all it takes, and Steam is now on the beta channel. Valve welcomes bug reports from testers, so if you run into an issue, use the "Report a bug" button in the Interface page.


Suggested Read 📖: Epic Games is looking to entice Linux gamers with its anti-cheat move.


from It's FOSS https://ift.tt/29mxpv0
via IFTTT

Kamis, 15 Oktober 2026

FOSS Weekly #26.42: AI in Kernel, Ubuntu 26.10 Firefox Business, Mint Release Changes and More Linux Stuff

FOSS Weekly

AI's role in kernel work is looking more apparent now. Linus Torvalds' use of Claude Code has tripled read speeds for concurrent file access, while Sasha Levin proposed an agents directory to house AI skills for kernel work.

And that's just the way AI is progressing, for good or bad. Last week's most popular news was an open source project that used AI to reverse engineer Adobe's Photoshop and other tools. Now the same project has used AI to 'clone' Microsoft Office.

These days, 9 out of 10 new open source software I come across is created with AI assistance. My inbox is flodded with new software review requests. One glance and I can 'feel' that both software and the coverage request email used AI.

So, like Linus Torvalds, I have made my peace with it. Until now, I was trying not to recommend open source tools that were openly developed with help of Claude or other AI tools. I don't see the point of it anymore now. If an open source software is good and I feel that readers would find it useful, I will feature it regardless. You can then decide on your own if you want to use it or not.

And this is also the time to get moving towards local AI. Where AI and models live in your system locally instead of a cloud. Sure, it won't match the performance of Claude and other frontier models, but some smaller tasks can still be achieved with local AI. Ubuntu's AI-based voice input tool Myna is a proof of that.

Do subscribe to the Local AI Weekly newsletter if you want to stay updated and use the AI on your system in true open source spirit.

This edition of FOSS Weekly is supported by PrivacyNotes, an open source, zero knowledge note management app.

CTA Image

Your notes, tasks, password, secrets. Keep them organized with open source tool, PrivacyNotes. Store them locally or encrypt them to a Swiss cloud. Start free, import the notes you already have, and see if it fits. If you want more storage with Pro later, it’s a one-time payment, not a subscription.

Try PrivacyNotes

📰 Linux news that matters

Ubuntu 26.10 is going to be released today. While we wait for Ubuntu 26.10 ISOs to appear, the next interim release already has a codename, "Tenacious T-Rex," marking the first time Ubuntu has ever used a dinosaur-themed mascot.

ONLYOFFICE Docs 10.0 brings AI assistance to every editor for text summarization and formula drafting, while adding collaboration features, spreadsheet speed improvements, and modular apps for forms and file management.

Strata is a new keyboard-first file manager for Omarchy and Arch that just hit 1.0, offering column view browsing, vi-key navigation, and a clever feature that remembers each folder’s sort order and icon size.

LibreOffice has come to the rescue after Microsoft's discontinuation of Publisher for 365 users. Using the Document Liberation Project’s reverse-engineered library, users can now open PUB files and migrate them to open standard formats.

Mozilla is targeting the commercial market with Firefox Enterprise, a product that would let organizations manage Firefox installations across employee devices through a self-hosted console.

Linux Mint has moved to an annual release cycle, with the next one, Linux Mint 27 "Adrien" arriving on Christmas. There won't be a Mint 23.x

The CachyOS team recently announced that Framework is increasing its support for the project, going from $250 per month to $850, taking the total figure up to $10,200 a year.

Open source boot firmware LibreBoot has a new release supporting more hardware now.

🧠 What We’re Thinking About

Six open source vendors have launched Open Productivity Software to expand openDesk from government use into the enterprise market.

🧮 Linux Tips, Tutorials, and Learnings

My Computer is a Shell extension that restores the unified "Computer" view that GNOME dropped from Files (Nautilus) in the GNOME 47 release. It displays drives, network locations, and removable media in one place rather than them being scattered across the sidebar.

Arch users run pacman -Syu for updates because it prevents dependency mismatches when the local package database is stale. Running just -S on an outdated system can leave you with incompatible package versions.

👷 Homelab and Hardware Corner

Pebble completed the full open source release of software, hardware schematics, and mobile apps in 2025, paving the way for its resurrection. Now the Pebble Round 2 smartwatch has entered production and begun shipping to preorders.

Zima, brand behind ZimaOS, ZimaBoard, and ZimaCube, is organizing a self-hosting event on Reddit where you can win homelab gadgets and AdGuard and PhotoPrism licenses just by sharing your self-hosting story. If you already self-host, why not try your luck? Or, at least explore how other people are self-hosting.

✨ Apps and Projects Highlights

BentoPDF is a privacy-first, open source PDF toolkit that processes files locally in your browser instead of uploading to servers.

A new open source GIS tool is here; it lets you chat with an AI Assistant about map data and geographic workflows.

If you like what we do and would love to support our work, please become It's FOSS Plus member. It costs $49 a year (less than the cost of a McDonald's burger a month), and you get free ebooks, an ad-free reading experience with the satisfaction of helping the desktop Linux community.

Join It's FOSS Plus

📽️ Videos for You

For people who are working extensively with git, this terminal-based git client is worth a try.

💡 Quick Handy Tip

0:00
/0:15

In the Nautilus file manager, you can carry out a search in the current folder using Ctrl+F or search everywhere using Shift+Ctrl+F. When you find the item you were looking for, you can use the shortcut Ctrl+Alt+O to open its location.

Going further, you can also use the shortcut Ctrl+. to open a terminal at that location.

🎋 Fun in the FOSSverse

Call yourself a true Arch Linux fan? Are you bold enough to prove it?

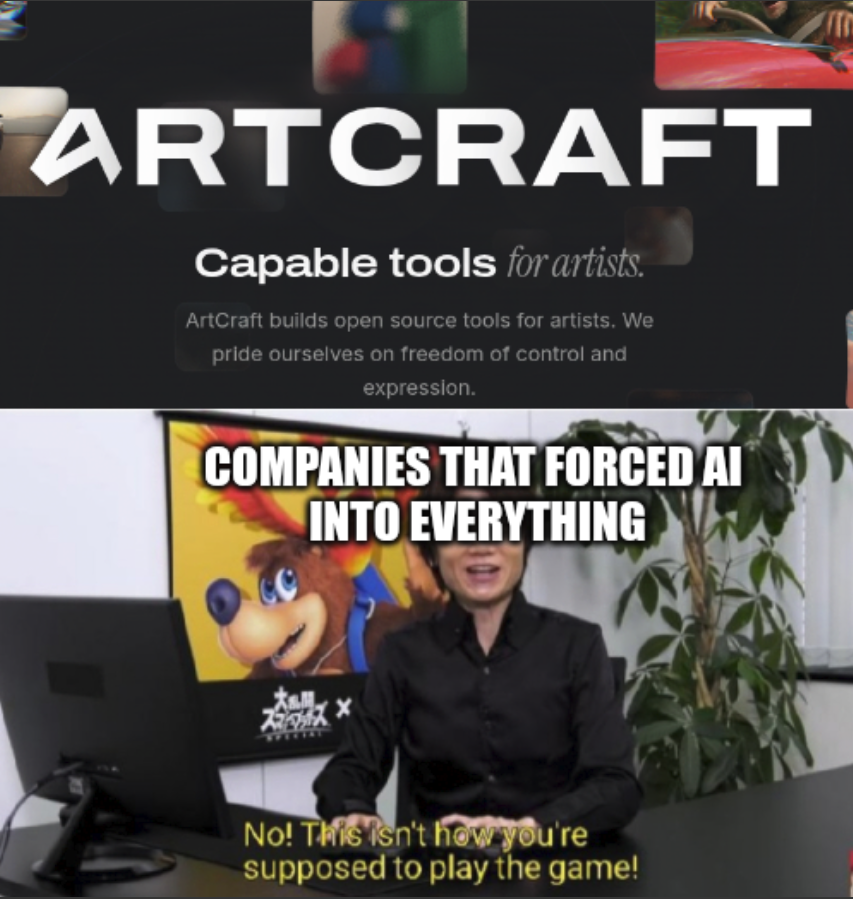
A reality check for big names like Adobe. 🤭

artcraft meme

🗓️ Tech Trivia: Long before IT became the industry we know today, British computing professionals were organizing themselves. On October 14, 1957, the British Computer Society was formally incorporated following a merger of two computing groups.

🧑‍🤝‍🧑 From the Community: A very interesting thread surrounding NixOS and Nix has popped up, featuring replies from supporters and skeptics.


from It's FOSS https://ift.tt/NfzSV8m
via IFTTT
Epic Games Wants Linux Gamers. It's Rebuilding EAC For Fortnite

epic games, fortnite and easy anti-cheat banner

Linux gamers have gotten used to hearing that yet another multiplayer title is cutting off the platform due to a variety of reasons, though most of their arguments usually sound lazy to me.

Take Ubisoft, for instance. They recently stopped For Honor from being playable on Linux and the Steam Deck, saying that they could not meaningfully deploy protection for the platform.

Now we have Epic Games swaying the other way, rebuilding its Linux anti-cheat under a new name while also offering a preview release for the long-requested native Epic Games Launcher.

Anti-cheat on Linux isn't some pipe dream

Easy Anti-Cheat has supported native Linux games since 2014 and Windows games running through Wine or Proton since 2021. Epic is now rebuilding that Linux implementation into EAC Linux v2, aiming to get much closer to Windows by leaning on security features Linux already has.

On Windows, EAC relies on a kernel driver that is active only during play. On Linux, EAC Linux v2 won’t have such a module acting in one of the most sensitive parts of the system.

That matters because kernel-level anti-cheat is a common sticking point for Linux gamers.

EAC Linux v2 runs a systemd service that stays active just for the length of a protected game session, alongside eBPF programs written by Epic that watch for tampering and cheats.

For players, this means a stricter boot setup, so Secure Boot and TPM 2.0 need to be on, the kernel has to be signed with a key Epic recognizes, and several other boot and kernel settings come into play.

EAC checks all of this only when a protected game launches, and failing the check brings up an error, not a ban. Players can also keep a separate boot entry for protected games and run their own keys elsewhere.

Testing the waters

Fortnite will be the first game to test EAC Linux v2, with plans to open it to other developers once the system is validated. Developers with games already on EAC for Linux can stay on the older version or switch.

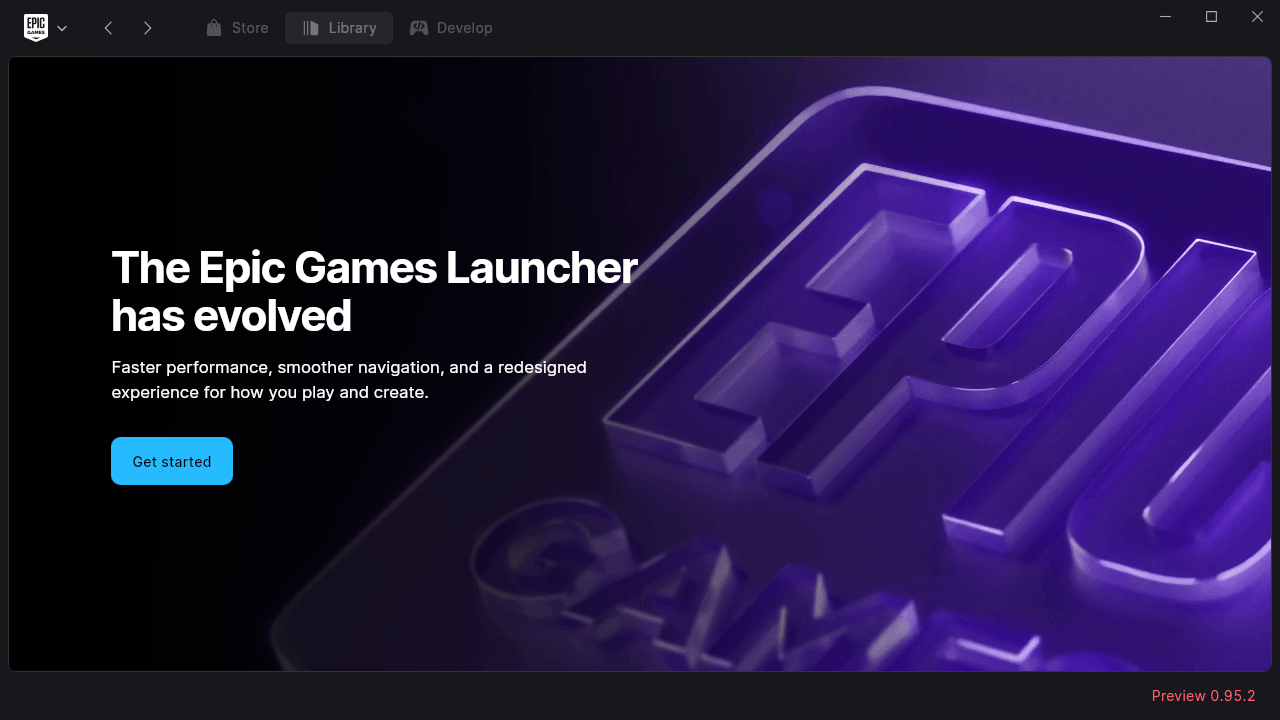
Getting Fortnite itself onto Linux depends on distro support. It will arrive through the new launcher (shown below) once enough maintainers meet the security requirements.

the epic games launcher for linux, preview version

The preview officially supports Ubuntu 22.04 LTS or newer, Fedora 43 or newer, and Debian 12 or newer, while other distros may work but are not officially tested.

The launcher itself runs natively, but many games are Windows-only, so they may need a compatibility layer like Wine or Proton to run.

The community needs to step in

Epic is reaching out to Linux community leaders and inviting distro maintainers to get in touch since protected games will only launch on systems booted with keys from a trusted list.

It is maintained in-house for now, with the goal of going open source sometime down the line.

They already seem to be in touch with Fedora, as a panel scheduled for later this year names Fedora Project Leader Jef Spaleta as a co-host, with the talk centered on enabling fair competitive gaming on Linux.

SteamOS is the next obvious name to bring up, but the Steam Deck doesn't meet the requirements yet. Talks with Valve are ongoing, with the aim of supporting the handheld later.

While it's still early, this is good news for gamers on Linux, as this is a platform that keeps getting shown the proverbial middle finger when it comes to gaming.


Suggested Read 📖: Last month, I spent some time with GeForce NOW on Linux to see if it's gameable.


from It's FOSS https://ift.tt/83v1e9o
via IFTTT